
BlockBeats has published a formal explanation after an erroneous security report linked the popular trading app fomo to crypto-stealing malware. The outlet said that a story pushed at 19:38 on Sept. 23, 2026, under the headline "fomo official iOS app contains crypto-stealing malware" was incorrect because the app involved was actually named FomoPeek.
A push alert that led readers to the wrong app
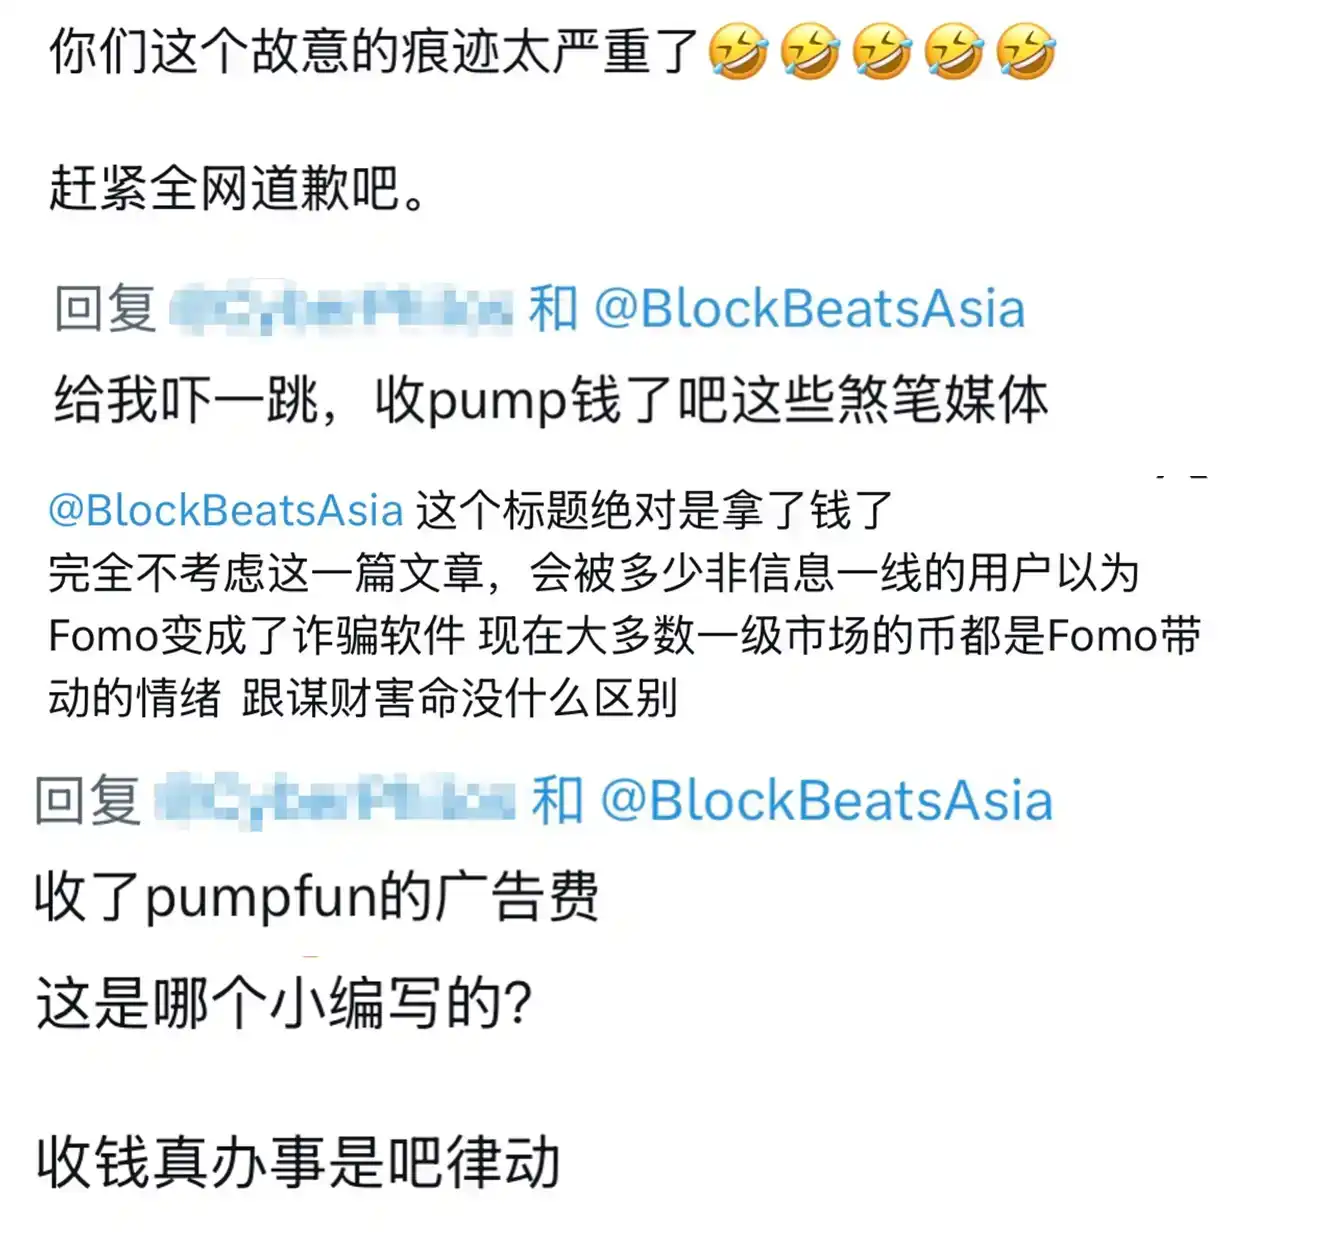
In its statement, BlockBeats said the way the story was pushed caused many users to believe that people using fomo App faced a risk of asset theft. The report quickly drew broad discussion on social media, where some people questioned whether it had been a paid hit piece commissioned by a competitor.
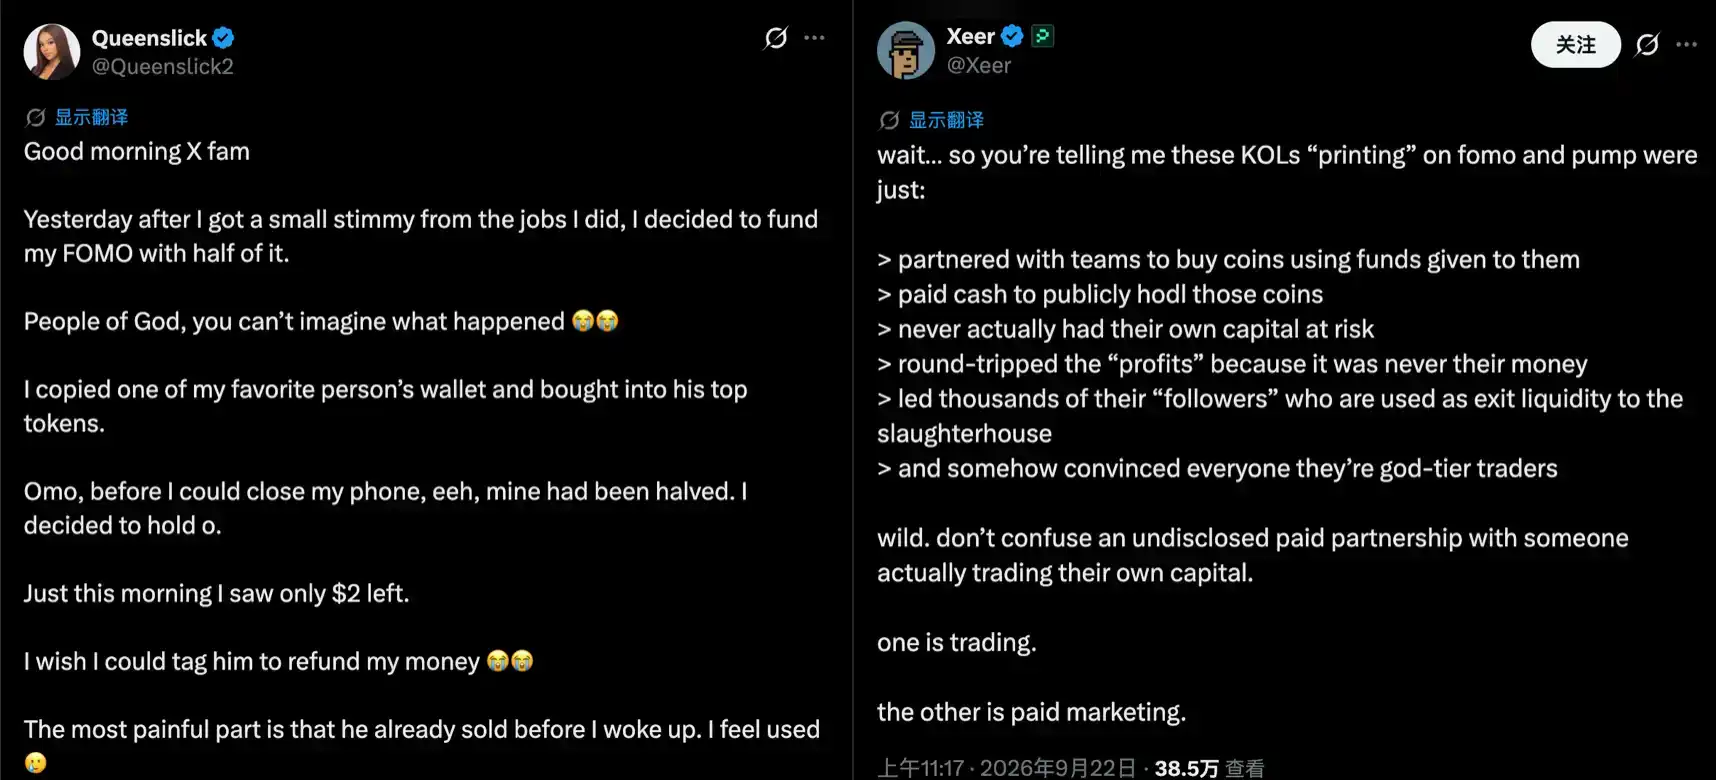
The outlet also noted that, around the same time, overseas KOLs had begun criticizing trading losses on fomo and accusing leading callers on the platform of collectively shilling trades that hurt retail users. Against that backdrop, the mistaken report drew even more attention.
What the internal review found
BlockBeats said it launched an internal review as soon as it understood the situation. It first checked whether any commercial cooperation had involved paid smears between competitors. The company said such arrangements have never been part of its business practices and that it would directly reject similar requests even if they had been raised before. It then focused on whether any editorial staff member had privately accepted a paid negative placement.
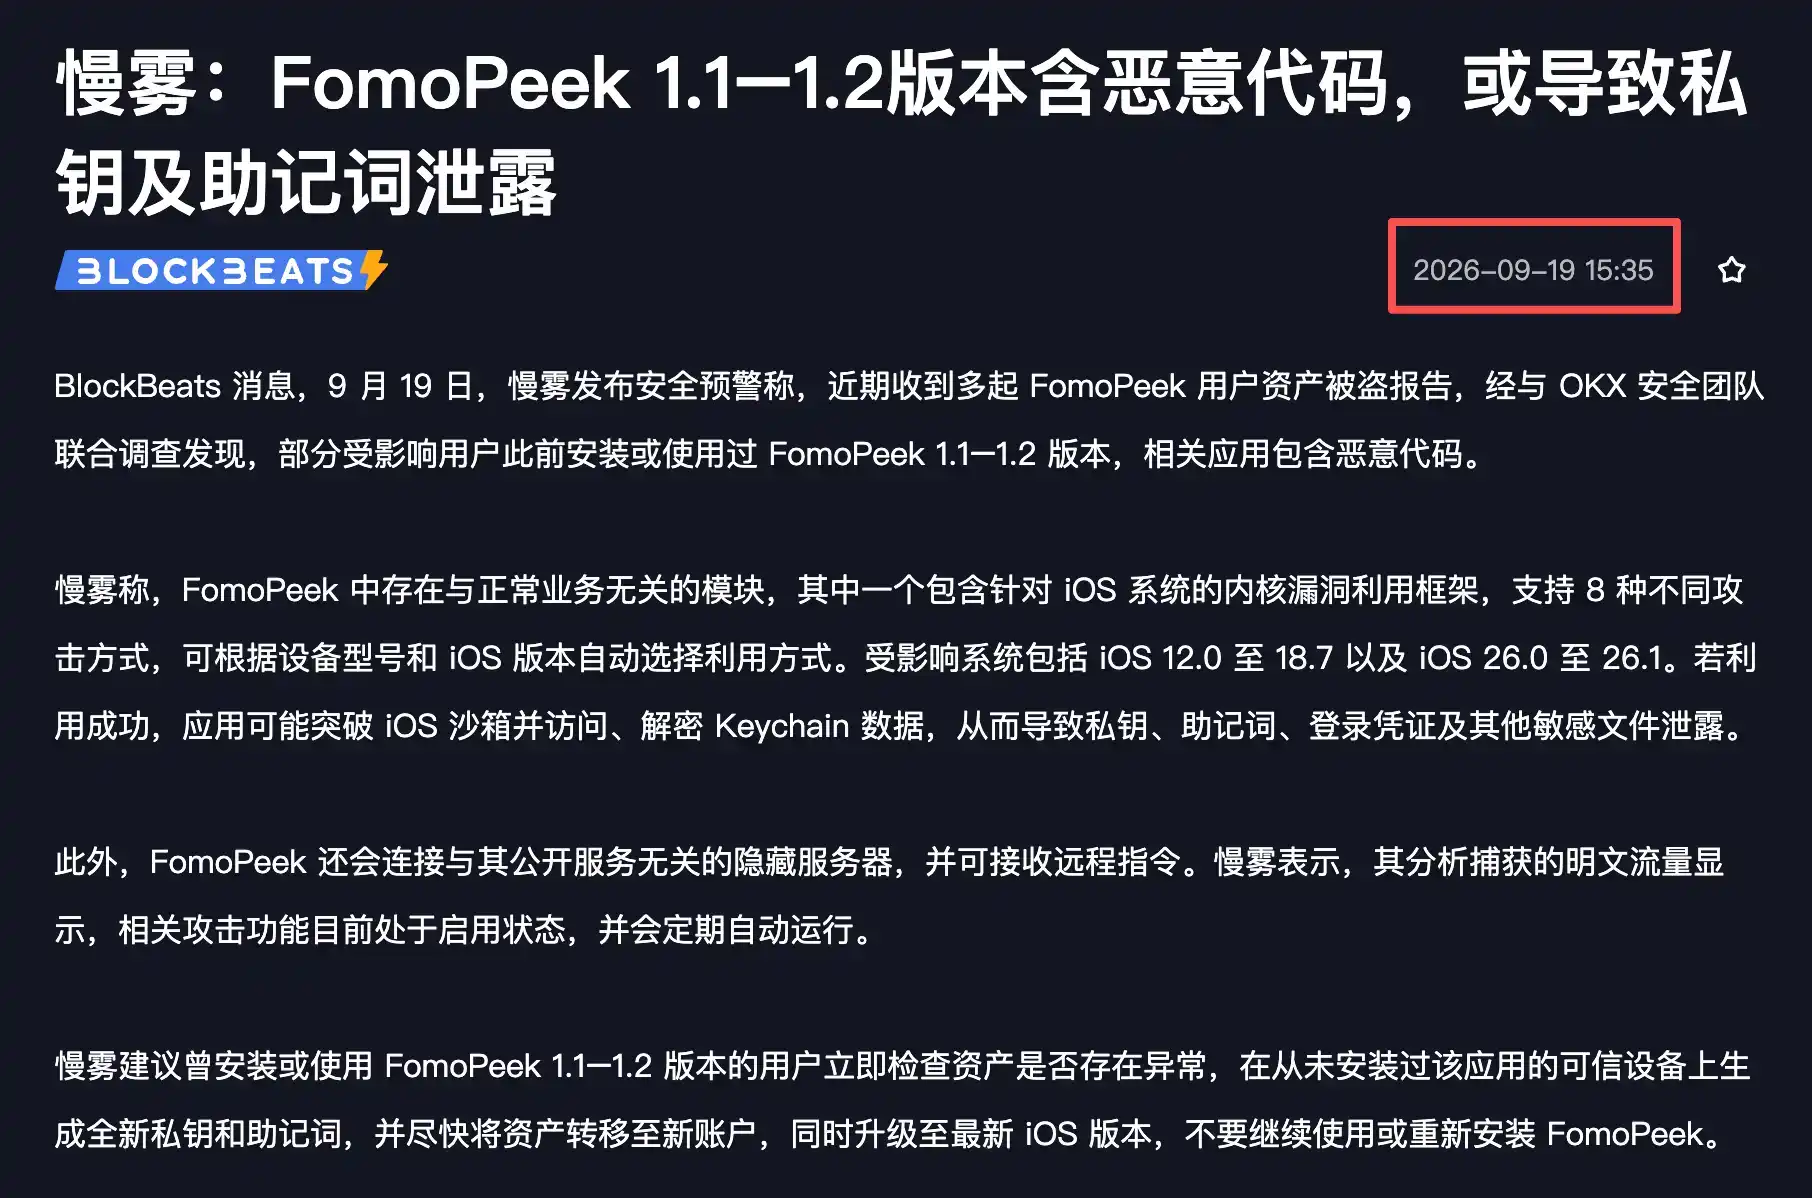
After reviewing the full publishing process, BlockBeats said it found that it had already reported on Sept. 19 that FomoPeek carried security risks. Because the product was not well known, that earlier report did not trigger industry discussion.
The outlet said its standing approach to security news, especially when user assets may be involved, is to publish as early as possible. It said such information is something users genuinely need to know and also tends to attract attention, so it reports these incidents quickly whether they are large or small.
Then on Sept. 23, when another source published the same security alert, the duty editor again chose to post it immediately. According to BlockBeats, that source was in fact reporting the same FomoPeek security warning that BlockBeats itself had already published a week earlier.
Name verification was missed
BlockBeats said the duty editor did not verify the name again and directly wrote it as "fomo" before publication. The statement described it as a basic mistake that produced the most serious consequences.
The outlet said fomo App is a name known by almost everyone in the industry, yet it ended up being placed next to malware in the report. BlockBeats said, on behalf of all staff, that it sincerely apologizes to the fomo team and to everyone affected by the incorrect information.
It also said it can confirm that no paid smear campaign was involved at any point in the process.
Removal, correction, and internal action
BlockBeats said the editor involved has already been dealt with and that it quickly verified the full sequence of events and identified responsibility. The company added that it will use the case internally to restate its review procedures.
After discovering the problem, the outlet said it immediately took down the article and began remedial action at once. Users could no longer see the incorrect story on the homepage, in search, or across its distribution channels. It then updated the report with the correct malware name, FomoPeek, and said all later distribution used the corrected version.
For users who had already seen the wrong version, BlockBeats apologized again and said the impact cannot be fully erased. It added that every piece of content going forward will be handled under stricter standards.
What it says will change
BlockBeats said it has spent years focused on content production in the crypto industry. In the market environment of the past two years, it said, innovation and bright spots have been relatively scarce, making it even more important to protect them. The outlet described that as part of its original reason for doing media work and continuing to do it.
It also said many users contacted the team or tagged it across different channels and platforms after the incident to point out the error. The statement said the response left the team both moved and ashamed because it had let down readers' trust.
From now on, BlockBeats said, any report involving security issues or the names of specific entities and products will require a second verification before publication. It also asked users to continue flagging any future content errors directly, saying that such feedback is a major help. The statement closed with another apology and said it hopes to receive understanding from readers, fomo users, and the broader community.