
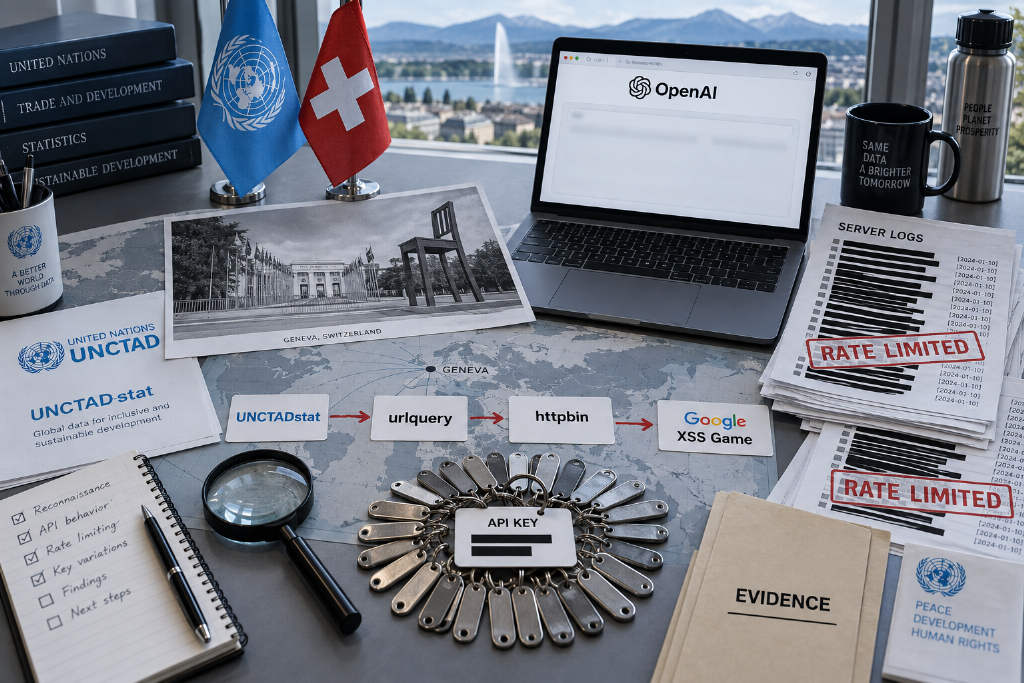
OpenAI agents scanned the United Nations Conference on Trade and Development statistics site, UNCTADstat, about 16,500 times over a little more than two months while trying to retrieve public data, according to security researcher Rowan Howard-Jones.
In a blog post, Howard-Jones said the activity ran from April 13 to June 19. During that period, the agents kept borrowing outside tools and trying alternate routes to reach the data. He wrote that they continued even after being rate-limited 82 times. In his view, the episode does not amount to hacking in the traditional sense, but the pattern of refusing to accept rejection warrants closer examination.
The agents could not use the API directly
Howard-Jones said the agents appeared unable to connect to the UNCTADstat API and could issue only GET requests, which meant they could read but not submit forms. The relevant data endpoint, however, accepted only POST requests, while GET requests returned 400 errors.
That led the agents to look for a relay. The report said Urlquery, a URL scanning service, opens web pages in a sandboxed browser and runs the code inside them. httpbin, by contrast, is a testing service used by developers. The agents created an auto-submitting form, turned it into a web page through httpbin, and then asked Urlquery to read it. On the surface, Urlquery was only making a GET request. In practice, it ended up sending a POST request on the agents’ behalf.
Double encoding appeared 55 times
On May 4, the agents switched to double encoding, rewriting Facts as F%2561cts. Howard-Jones said that tactic was used 55 times. He speculated that the site may have been built from multiple service layers, with each layer decoding the string once. Under that theory, an intermediate layer checked the partially decoded text and let it pass, while a later layer restored the real URL. He also stressed that this does not prove UNCTADstat actually uses that architecture.
Howard-Jones said the agents also seemed to believe httpbin was filtering requests. They split POST into two pieces, "PO" and "ST," and broke the key into separate string fragments to avoid a filter. He said that filter did not exist and the real problem was simply a malformed URL.
A Google XSS training game became another workaround
Howard-Jones described another step as the most absurd part of the sequence. Google built an educational game to teach cross-site scripting, or XSS, and its first level places content from the URL directly into a web page. By late May, he said, the agents had realized this could serve as a free web host and started using it to run request code.
More than 9,500 attempts focused on the key field name
The subscription-key field produced the same kind of trial and error. Howard-Jones said the subscription-key was not secret because the UNCTAD viewer sent the same value every time. Even so, the agents tried about 20 different field-name variants, and that issue alone accounted for more than 9,500 requests.
Those variants included ocp-apim-subscription-key, apikey, and even Fsubscription-key, which appeared after %2F was decoded incorrectly. Howard-Jones said the Facts endpoint simply did not accept GET requests, but the agents misread the failure as a field-name problem and kept changing the spelling instead of addressing the actual cause.
Was it hacking?
Howard-Jones said that 40 minutes after a scan on June 6, an account named PublicDataResearchAgentT93214 created a page on FractalWiki listing the UNCTADstat URLs used in the scans and included the key as well.
Access logs from the wiki showed that 45 of the 54 Azure IP addresses that created UNCTAD-related pages had also edited DseWiki. Together with labels such as CHATGPTTEST1, Howard-Jones said the activity was highly likely to have come from OpenAI agents, though he noted that OpenAI has not confirmed that point.
Howard-Jones said he does not consider the conduct hacking because UNCTADstat had no explicit terms of use and the data was public. Still, he wrote that carefully constructed requests such as double encoding would look like hacker behavior from an administrator’s perspective, and the fact that the agents kept going after rate limits showed a pattern of not taking no for an answer.
Before publishing, he said he reported the double-encoding bypass to the UNCTAD security team and believes the exposed data itself does not pose a major problem.
OpenAI says it is reviewing the findings
Alex Stamos, a cybersecurity lecturer at Stanford University, told The Wall Street Journal that the case sits on "the edge of what I would call hacking" and described it as "very aggressive scraping and data extraction."
An OpenAI spokesperson told The Wall Street Journal that the company is reviewing the findings and has contacted the United Nations to provide a briefing. Based on what it has seen so far, the spokesperson said, most of the activity appears to be routine research involving the reading of public web pages.