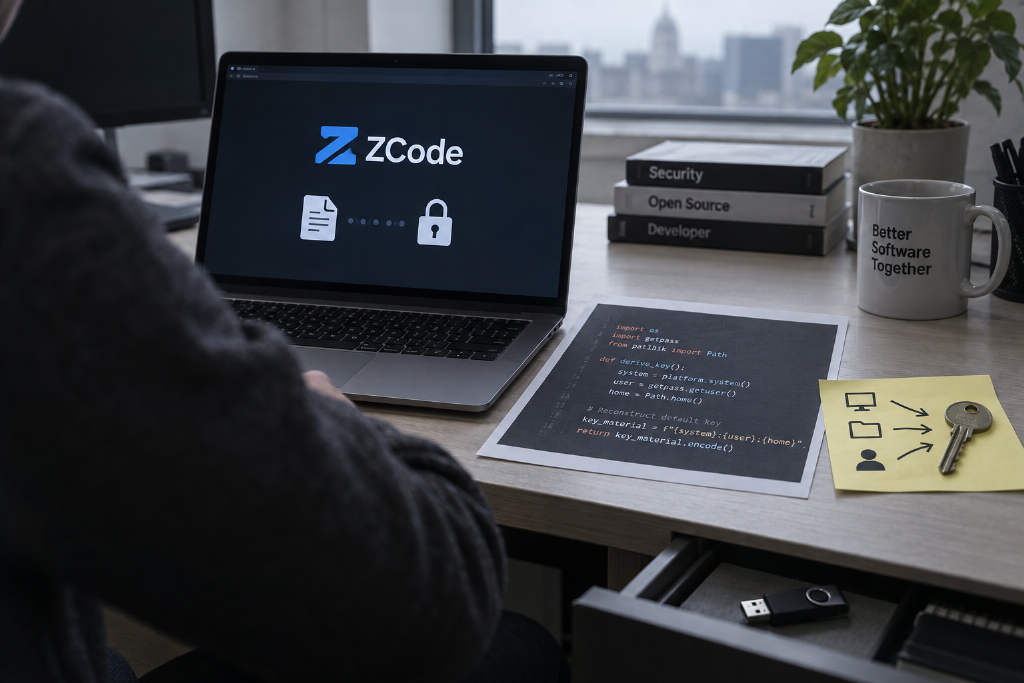
ZCode open-source release reveals credential security flaw in default key generation
A new security issue has surfaced after ZCode was open-sourced. Developers reviewing the code found that ZCode stores login credentials locally in encrypted form, but under the default setup, the decryption key can be derived directly from the operating system, username, and user directory. Those inputs are typically not hard to obtain. If an attacker gets access to the local credential file, the public source code would allow them to recreate the key without breaking the encryption algorithm itself. The finding also appears to conflict with ZCode’s documentation, which says the credentials are encrypted on a per-device basis and cannot be decrypted after switching machines. In the open-source default implementation, however, there is no use of a device ID or hardware-based information. That said, the issue is not described as a remote vulnerability. An attacker must first obtain the local credential file. Users who manually set ZCODE_CREDENTIAL_SECRET are also not affected by the default key path. If the file is exposed, login sessions for ZCode, Z.ai, or BigModel could be restored and then abused, including possible use of Coding Plan quotas, but the issue would not let an attacker compromise the computer itself.