How EIP-7702 Became a Critical Link in the Binance Hot-Wallet Theft
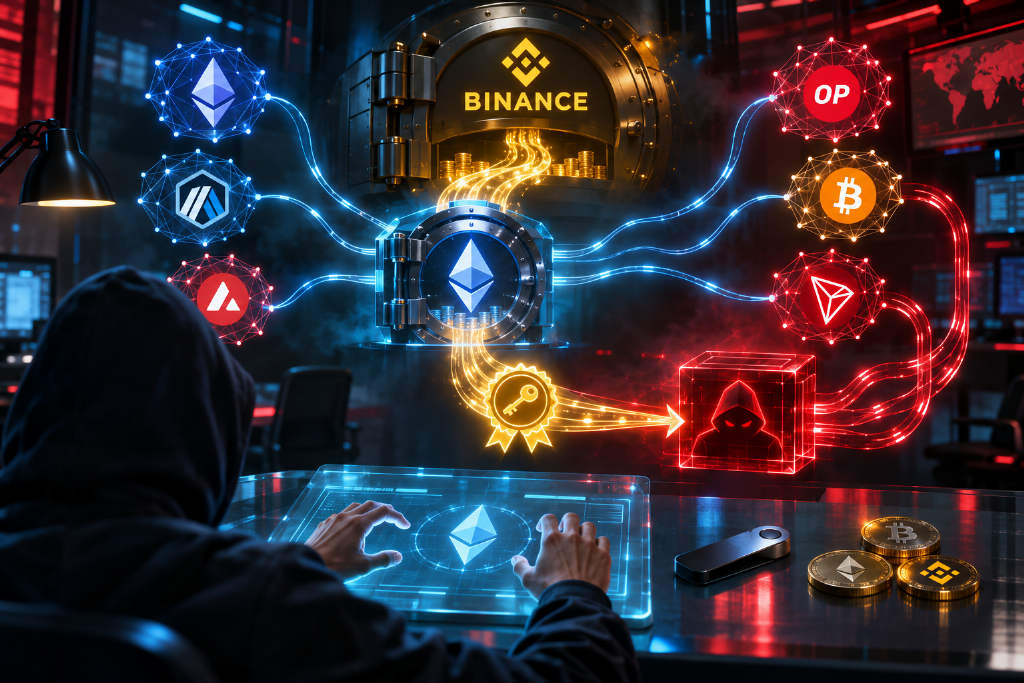
A Blockaid review says attackers stole at least $6.3 billion from Binance hot wallets across Ethereum, Arbitrum, Avalanche, Optimism, Bitcoin and Tron on Oct. 29, 2026. The attack centered on Binance 14, an Ethereum wallet that held roughly $2.5 billion before it was drained in a single transaction. Minutes earlier, the attackers used a leaked private-key copy to sign an EIP-7702 authorization that delegated the wallet to a malicious sweeping contract. The authorization was selected from a batch of 50 signatures covering consecutive nonce values. Only one matched, but that was enough to give the attackers ongoing code-level control. The attacker later used the delegated wallet to drain new deposits and call a Circle smart custody account. Tether and Circle froze about $1.8 billion in the attacker’s main receiving address, while native assets such as ETH, AVAX, OP and ARB could not be frozen by centralized issuers. Blockaid says the incident shows why exchanges need controls before signatures are produced and continuous on-chain monitoring after funds begin moving. A leaked private key can authorize a conventional transfer, but under EIP-7702 it can also create a persistent delegated account that remains dangerous after the initial sweep.