SlowMist flags GaslessReservoirEnabler flaw after about $23,000 in WETH and ZED is drained
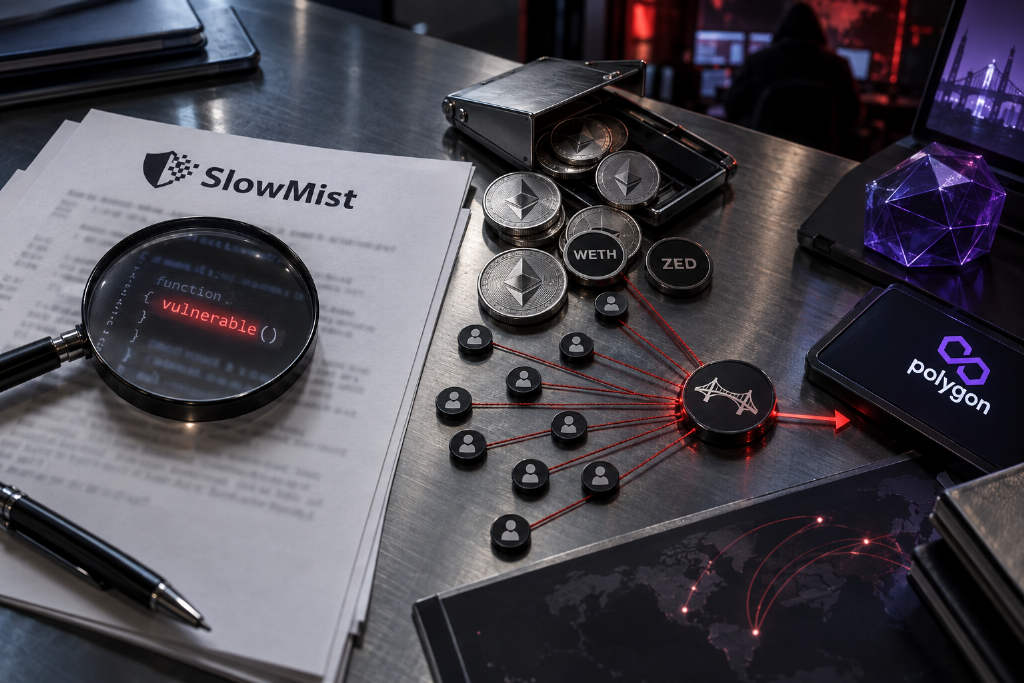
SlowMist disclosed a smart contract security incident involving the GaslessReservoirEnabler contract, saying a flaw in its erc20WithTransfersAndExecute function allowed an attacker to move about $23,000 worth of WETH and ZED. According to the security firm, the issue stems from the _executeInternal function, which checked the module address but did not bind ERC20 transferFrom instructions to the authorized asset owner. That design let any caller spend an existing allowance from victims as long as the token was on the whitelist. SlowMist said the attack affected 997 token holder addresses. It identified the attacker address as 0x46f54c1a86575679fc3d29666c1717e9786279aa and the affected contract as 0x9b58fdadc16e30fba313e044bf9e88689c3f163e. The stolen funds have since been consolidated and deposited into a cross-chain bridge on Polygon, according to the disclosure cited by Techub News.