imToken
21 days agoNews Editor

imToken launches imToken Stake brand for ETH staking

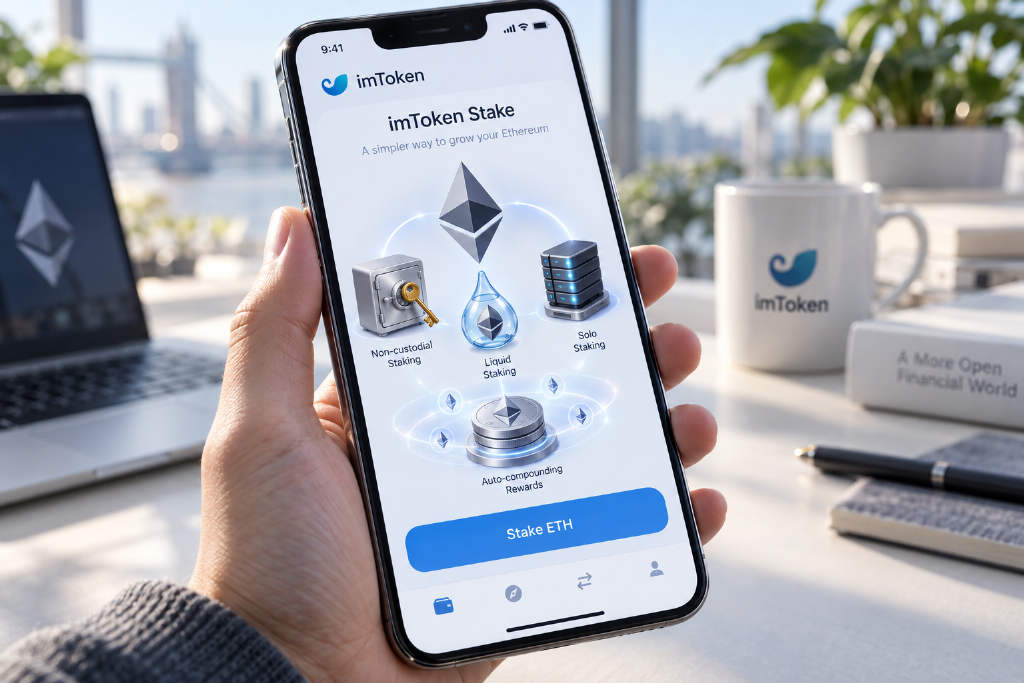
Decentralized wallet provider imToken has introduced a new ETH staking brand, imToken Stake, focused on Ethereum staking use cases. The offering includes three participation options: non-custodial staking, liquid staking, and solo staking. According to the announcement cited by ChainCatcher, the product is designed for several types of ETH holders, including long-term holders with 32 ETH or more, users seeking smaller and more flexible participation, and technically inclined users who want to run validators on their own. In the non-custodial staking model, users can complete the staking process inside the wallet while retaining control over withdrawals. Validator deployment, operation, monitoring, and maintenance are handled by imToken together with professional node infrastructure service providers. imToken also said its non-custodial staking service now supports a compound mode, allowing users to create compound validators so staking rewards can continue accumulating and be automatically restaked to improve long-term capital efficiency. The company said imToken Stake will keep focusing on security, autonomy, and transparency.
610
imToken launches imToken Stake brand for ETH staking
ETH
2 months agoNews Editor

For Long-Term ETH Holders, the Real Choice Is Yield From Staking or Liquidity From Borrowing

Odaily’s latest market analysis looks at a question many Ethereum holders now face after the network’s shift to proof-of-stake and the maturation of on-chain lending: if you plan to keep your ETH, should it be staked for protocol rewards or used as collateral to borrow stablecoins? The piece argues that the comparison is often framed too narrowly around APR, even though the two strategies serve different purposes. Native staking is designed for investors who are comfortable locking in a long holding period and want that time to generate additional ETH through protocol-level rewards. Borrowing against ETH, by contrast, is about unlocking liquidity without selling the underlying asset, which introduces debt, variable borrowing costs, and liquidation risk. The article also notes that Ethereum’s Pectra upgrade changed the staking equation by raising the maximum effective balance for a single 0x02 Compounding Validator from 32 ETH to 2048 ETH, allowing rewards above 32 ETH to be added in 1 ETH increments and compounded. It further points to imToken’s non-custodial native staking product as an example of how wallet tools are trying to lower the operational barrier for users who want validator exposure without handing over key control.

760
For Long-Term ETH Holders, the Real Choice Is Yield From Staking or Liquidity From Borrowing
stablecoins
2 months agoNews Editor

Stablecoins and RWA Are Moving From Tokenized Assets to Real-World Payments

A Foresight article argues that the story around stablecoins and real-world assets, or RWA, is shifting away from simply issuing more tokens and toward building a financial network that can actually function end to end. The piece says the market is now focusing on whether tokenized assets can be issued in compliance, traded with investor rights intact, settled onchain, and eventually used in everyday payment scenarios. It points to several recent developments across traditional finance and crypto. The New York Stock Exchange said in January that it was developing a tokenized securities platform designed to support shareholder rights, 24/7 trading, fractional shares, instant settlement, and stablecoin-based cash settlement. Later, it brought in Securitize and tZERO to add infrastructure around transfer agency, broker-dealer services, securities registration, and onchain settlement. On the crypto side, Bitfinex Securities recently launched five products that give qualified investors economic exposure to listed companies including Strategy and Metaplanet. The article also highlights a payments push in Japan. HashPort and Lawson tested an in-store yen stablecoin payment in Tokyo in August, while NETSTARS completed a Stablecoin Pay proof of concept at another Lawson store. On Sept. 3, imToken and NETSTARS signed an MOU to explore connecting imToken wallet infrastructure with Stablecoin Pay.

1010
Stablecoins and RWA Are Moving From Tokenized Assets to Real-World Payments
OpenClaw
2 months agoNews Editor

OpenClaw 2.0 puts the spotlight on verifiable authorization for autonomous agents

OpenClaw released version 2.0 on Aug. 30, describing it as the largest update in its history, with more than 16,000 pull requests spanning installation, messaging, memory, Skills, models, Automations, browser control, native apps, Plugins, and security. The release has renewed attention on a broader shift in the agent stack: AI agents are no longer limited to generating text and are gaining the ability to act on external systems. That shift creates a trust problem that existing permission models struggle to handle. Full delegation, such as handing over a private key or a long-lived Session Key, can maximize automation but concentrates risk if prompt injection, malicious webpages, environmental contamination, or model misunderstanding leads to unintended actions. At the other extreme, requiring approval for every step protects users but strips much of the value from automation. The article argues that the industry now needs finer-grained, verifiable authorization. It points to imToken’s exploration of Sigil, which aims to separate tool access from approval for a specific action. The proposed framework centers on clear, parameter-bound consent under the principle of "What you see is what you sign," using mechanisms such as Passkey, biometrics, one-time signatures, short validity windows, and request binding to ensure that what the user approved matches what the system actually executes.

970
OpenClaw 2.0 puts the spotlight on verifiable authorization for autonomous agents
Ethereum
3 months agoNews Editor

Ethereum staking reaches 34.7% of supply as users weigh solo, native, liquid and exchange options

Ethereum staking has climbed to a new high, with about 42.4 million ETH — roughly 34.7% of total supply — locked in staking as of late August, according to the source article by imToken published by Foresight. More than 2.2 million ETH was also waiting in the validator entry queue, implying a roughly 39-day activation delay at the current pace. At the same time, traditional finance is moving deeper into the market: in August, Fidelity advanced staking arrangements for its Ethereum fund FETH, signed custody-related agreements with Anchorage Digital and BitGo, and set out a mechanism for distributing staking rewards. The article argues that Ethereum staking is no longer just a way to lock tokens for yield. With changes such as Pectra’s 0x02 validator model, liquid staking through Lido, non-custodial native staking services, and exchange-based products, staking is increasingly being presented as a broader on-chain asset management framework. The key question for ETH holders is no longer simply whether to stake, but which path to choose. The trade-offs differ across solo staking, native staking, liquid staking, and exchange staking, especially in terms of control over withdrawal rights, operational burden, liquidity, protocol design, and exposure to third-party risk.

1470
Ethereum staking reaches 34.7% of supply as users weigh solo, native, liquid and exchange options
AI Agent
3 months agoNews Editor

AI agents are getting closer to live trading, but simulation and wallet controls still sit between testing and real capital

A new crop of infrastructure is pushing crypto AI agents beyond tool use and toward actual task execution, especially in trading. In OdailyHot’s analysis, the shift is not just about smarter foundation models. It is about whether an agent can operate in a changing environment, absorb feedback from prior decisions, and keep adjusting without direct human intervention. The article points to three pieces moving into place. SKALE’s AgentPit, launched in mid-August, mirrors Polymarket market data and API access inside a simulated trading sandbox that uses a production-like CLOB order book, CTF tokens, and settlement logic, but swaps real funds for simulated USDC. Amazon Bedrock AgentCore Payments reached general availability on Aug. 18, allowing agents to autonomously pay for third-party APIs, MCP services, and data sources with support for stablecoins and x402. Binance followed on Aug. 20 with Agent OS, exposing agent-native interfaces for market data, accounts, wallet functions, and supported trading actions under user authorization. OdailyHot argues that this stack still leaves one critical layer before agents can safely handle real money: the wallet. The core challenge is not handing private keys to AI, but granting tightly bounded execution rights without surrendering final asset control. That is where policy limits, account isolation, session keys, and user override mechanisms become central.

1370
AI agents are getting closer to live trading, but simulation and wallet controls still sit between testing and real capital
AI Agent
4 months agoNews Editor

From Blindly Saying Yes to Verifiable Approval: How Sigil Adds a Security Guardrail to AI Agents

As AI agents move from answering questions to taking real actions on behalf of users, authorization is becoming a critical security layer. In this article, imToken’s new “Sign” narrative is examined through Sigil, an early proof-of-concept product designed to sit between AI agents and wallets. The core issue is that many agents still rely on vague chat-based approvals such as “Yes” or “Confirm,” even when the underlying action may involve fund transfers, token approvals, contract calls, code execution, or access to sensitive services. That model creates three major risks: users often cannot see the exact parameters of what they are approving, a chat reply is not equivalent to a cryptographic signature by the account owner, and the approval interface itself can be manipulated by the same agent that initiates the request. Sigil’s answer is to rebind display, signing, and execution into a verifiable flow. Low-risk actions can proceed under predefined policies, while sensitive operations trigger a pause and generate a structured approval card sent through Telegram. The user must then confirm with Passkey and biometric authentication before the action can continue. The article also highlights Sigil’s three protection layers: clear presentation of real request parameters, proof that only the actual user can approve, and an isolated confirmation module anchored on-chain and rendered in a sandbox to prevent interface forgery. While the need is most obvious in crypto, the framework may extend to email, files, terminals, identity usage, payments, and broader agent permissions.

870
From Blindly Saying Yes to Verifiable Approval: How Sigil Adds a Security Guardrail to AI Agents
imToken
4 months agoNews Editor

imToken’s Sigil Adds a Verifiable Signing Guardrail for AI Agents

As AI agents evolve from answering questions to taking real-world actions, the weakest link is no longer task execution alone, but user authorization. In many current agent workflows, users approve sensitive actions with a vague chat reply such as “Yes,” without seeing the exact trading route, pool selection, slippage, protocol calls, wallet used, token approvals, or final transaction parameters. imToken addresses this gap through its newly emphasized fourth “S” in its brand framework—Sign—alongside Store, Send, and Stake. Its early proof-of-concept product, Sigil, is designed to place a security layer between AI agents and wallets so that high-risk actions can only continue after a clear, independent, and verifiable user approval. The system combines policy-based execution boundaries, structured approval cards delivered through Telegram, Passkey-based signing with biometric verification, and an execution model that binds display, signature, and final request together. Sigil also separates confirmation rendering from the agent itself through a registered module, on-chain-fixed content, sandboxed rendering, and hashed request binding. While the immediate use case is crypto transactions, the underlying model extends naturally to broader AI agent permissions, including data access, identity use, file modification, publishing, purchasing services, and automated task execution.

960
imToken’s Sigil Adds a Verifiable Signing Guardrail for AI Agents
Total 23 items
Go topage