
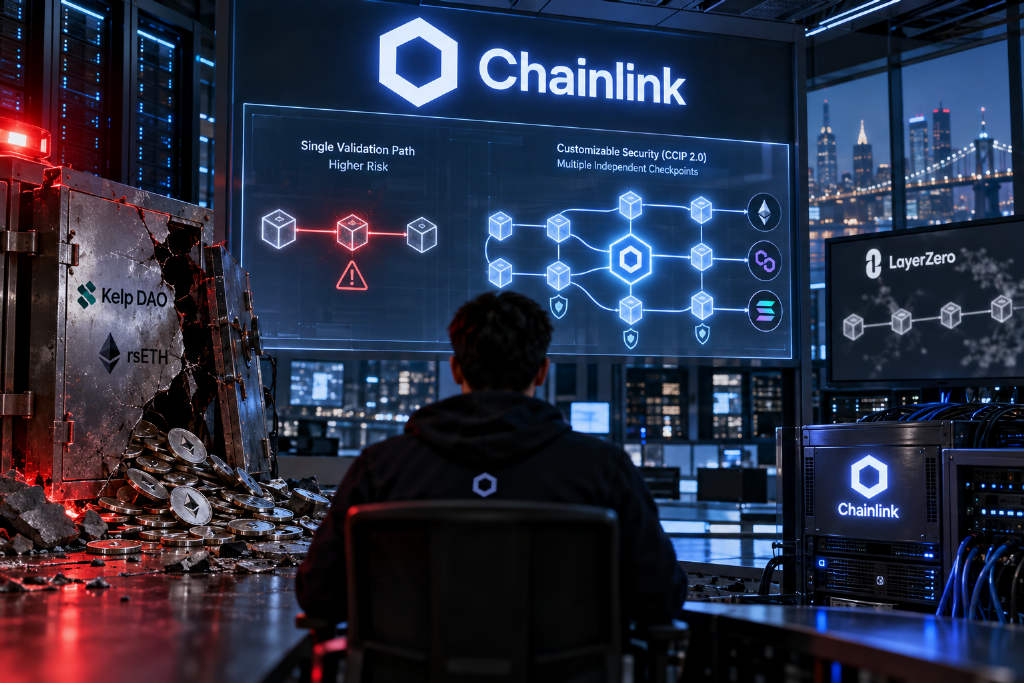
Chainlink on Monday released CCIP 2.0, an upgraded version of its Cross-Chain Interoperability Protocol that expands how blockchains exchange messages and move funds. The new software allows companies to add their own security checks to transfers, on top of Chainlink’s default verification system made up of 16 node operators.
The release comes five months after the year’s largest DeFi hack, an April attack on Kelp DAO that was tied to a bridge configuration using a single verifier. About $292 million in rsETH was drained in that incident, and Kelp later said it would migrate the token to Chainlink.
CCIP 2.0 adds customizable verification options
Chainlink is best known for its oracle network, which supplies blockchains with outside data such as asset prices used by lending and trading applications. CCIP, first launched in 2023, extends that business into moving tokens and messages across chains.
Because blockchains cannot communicate directly, moving a token from one network to another requires a bridge. Those systems depend on verifiers to confirm that a transaction actually occurred on the source chain before funds are released on the destination chain. If a verifier is deceived, an attacker can withdraw assets that were never deposited in the first place.
CCIP 2.0 introduces a menu of verifier options. Companies can run their own verifiers or use outside providers such as Infosys and Nethermind. Chainlink’s own network of 16 independent node operators still checks every transfer, regardless of what additional verification layers a user chooses to add.
Users should not need to be 「cross-chain security infrastructure experts」, the company told CoinDesk.
In a statement, Chainlink Labs Chief Business Officer Johann Eid said, 「Historically, legacy bridges have lost billions due to insecure infrastructure, while in-house builds are slow and expensive.」
Kelp DAO attack sharpened focus on bridge design
In April, attackers allegedly linked to North Korea’s Lazarus Group drained about $292 million in rsETH from Kelp DAO’s bridge. The bridge ran on LayerZero, and the attackers succeeded after tricking the single verifier used in that setup.
LayerZero said Kelp was responsible because it had chosen to use one verifier instead of several. Kelp responded that LayerZero staff had reviewed the configuration and never raised objections. CoinGecko data showed that nearly half of active LayerZero applications used the same one-verifier arrangement. Kelp later said it would move rsETH to Chainlink.
Risk Management Network no longer serves as a separate backstop
The release also changes a safeguard that Chainlink had previously emphasized. Its Risk Management Network, once described as a separate set of nodes that performed a second check on transactions, no longer fills that role in CCIP 2.0.
Chainlink said that independent check can now come from optional verifiers added by users. In practice, that suggests a user who adds nothing extra now appears to rely on one verification network, whereas the earlier setup had two.
Existing Chainlink users were automatically migrated to the new version. The company has not identified any institution using the new verifier setup so far. It said only that Aave and Maple have started adopting some of the upgrade’s other features.