
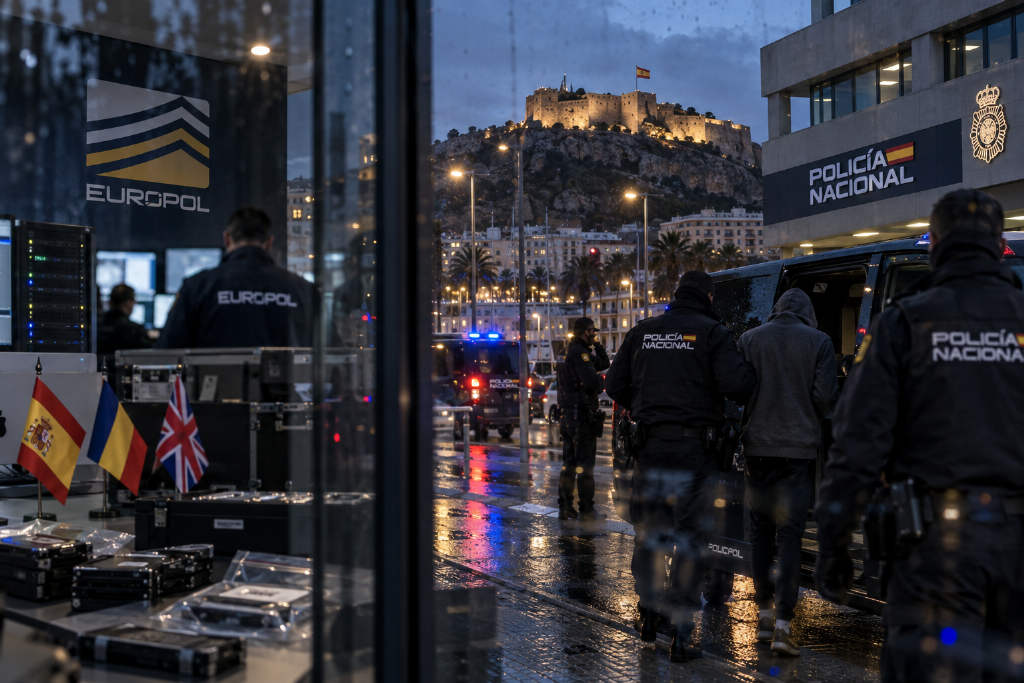
Spanish police have arrested a 16-year-old Romanian suspect in Alicante who is believed to have acted as an administrator and key operator of the ransomware group KillSec, according to Decrypt, citing a notice from Europol.
Two other suspects in their twenties were arrested separately in the UK and Romania. Investigators also identified a developer who turned 18 in August this year, but that person was not arrested because part of the alleged offenses took place while they were still a minor.
Operation KillSwitch reviewed around 1,000 suspected attacks
The operation, named Operation KillSwitch, was led by the Hamburg State Criminal Police Office and the city’s public prosecutor’s office in Germany. The investigation covered about 1,000 suspected attacks worldwide, and around 500 of them have been confirmed as successful intrusions.
Law enforcement searched eight locations in Spain, Greece, Romania, and the UK. Authorities took control of five central servers, redirected associated domains to seizure notice pages, and seized at least 110 TB of stolen data.
Group allegedly active since 2024
According to the notice, KillSec has been active since around 2024. The group allegedly broke into corporate systems by exploiting software vulnerabilities and weakly secured cloud storage entry points, copied internal data, and named victim organizations on dark web leak sites while demanding cryptocurrency ransom payments in exchange for not publishing the files. If victims refused to pay, the data was released for free.
Swiss federal police said the group also used double extortion tactics, encrypting servers before pressuring victims.
US indictment names a UK-based Dutch national
US prosecutors alleged that Fouad Eltibrizi, a Dutch national living in the UK and known by the alias Archduke, was indicted by a federal grand jury in Puerto Rico on Sept. 16. He was later arrested and is awaiting extradition. The maximum penalty he faces is 10 years in prison.
Europol’s European Cybercrime Centre is assisting the case with cryptocurrency tracing and digital forensic work.