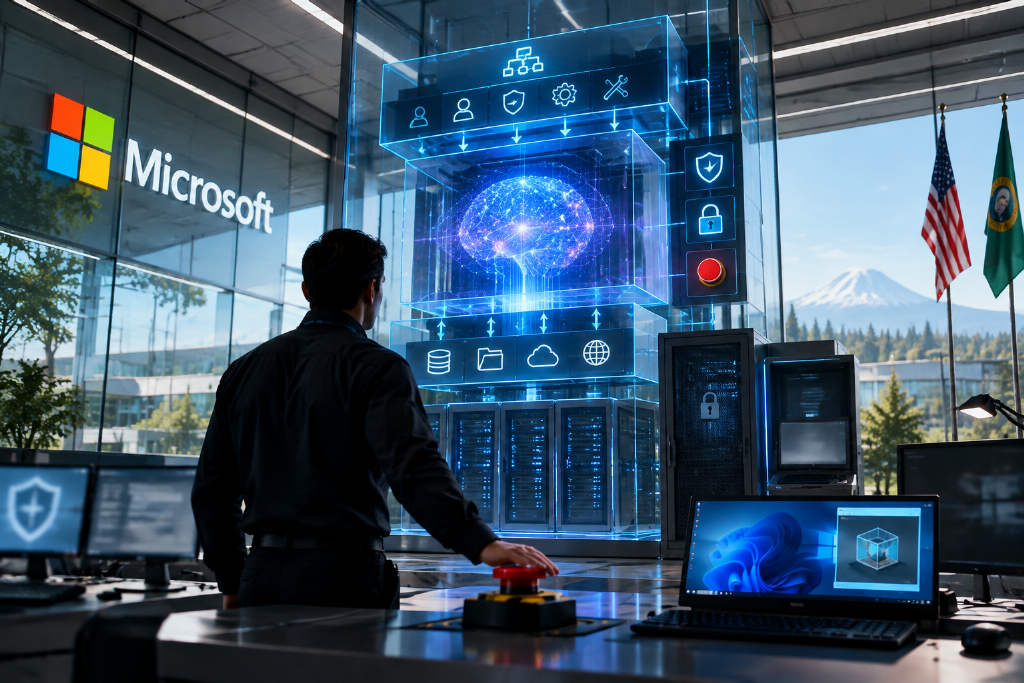
Microsoft CEO Satya Nadella said in a lengthy post that companies should handle AI models as part of internal security risk management rather than relying on vendor assurances alone. He argued that models can make mistakes even without malicious intent and can also be exploited by attackers, especially when they are allowed to read sensitive data or carry out critical actions on a user’s behalf. Nadella said the model should be separated from the harness, or agent execution framework, that schedules and runs tasks. Access to data and tools, he wrote, should be controlled by external systems. He also called for tamper-resistant logs for every critical action so human reviewers can inspect what happened. Nadella said chain-of-thought output should be visible, while acknowledging that such reasoning traces may not be reliable. His strongest point was that companies should assume from deployment that a model could be compromised and isolate it accordingly. Authorized personnel, he said, must be able to pause or shut down an agent while it is running, effectively giving it an emergency brake. Microsoft also announced this month that its MXC isolation tool is now generally available on Windows, using external policies to limit which files and network resources an agent can access.
Microsoft CEO Satya Nadella said companies should treat AI models as an internal security risk management issue, arguing that a model can make mistakes even if it has no malicious intent and can also be used by attackers.
He said businesses should not rely only on security assurances from model vendors, especially when a model can read sensitive data or carry out critical actions on a user’s behalf.
Separate the model from the agent execution framework
Nadella said the model should be separated from the harness, the agent execution framework used to schedule tasks. What data a model can read and which tools it can call should be controlled by external systems rather than by the model itself.
He also said every critical action should leave a tamper-resistant record that humans can review.
Chain-of-thought should be visible, but not treated as fully reliable
Nadella said chain-of-thought, or the reasoning process shown by the model, should be transparent. At the same time, he acknowledged that this material may not be reliable.
Assume compromise from the start of deployment
In his strongest warning, Nadella said companies should assume from the moment of deployment that a model could be compromised and should isolate it accordingly. Authorized personnel must be able to pause or shut down an agent while it is executing tasks, effectively giving the system an emergency brake.
He also said a model cannot audit its own behavior. Companies should keep testing for failures and attacks and disclose incidents in a timely manner.
Microsoft says MXC isolation is now available on Windows
Microsoft announced this month that its MXC isolation tool is now formally available on Windows. The tool uses external policies to restrict the files and network resources an agent can access.
This article was originally published by Bit.Fan. For more cryptocurrency news and market insights, visit www.bit.fan. Disclaimer:
The market information, project data, and third-party content displayed on this platform are for industry information sharing only and do not constitute any form of investment advice or return commitment.
Cryptocurrency trading carries high risks. Users should fully assess their risk tolerance and make independent decisions. All profits, losses, and legal responsibilities are borne by the users themselves.