
NEAR Intents has suffered another security breach, with about $3.8 million in assets stolen. The team said the incident was caused by a vulnerability in the interaction between its Omni deposit-and-withdrawal infrastructure and NEAR Intents smart contracts. After detecting abnormal activity, the protocol paused services. It said the contract-side issue was fixed in about an hour and that affected users will be fully reimbursed.
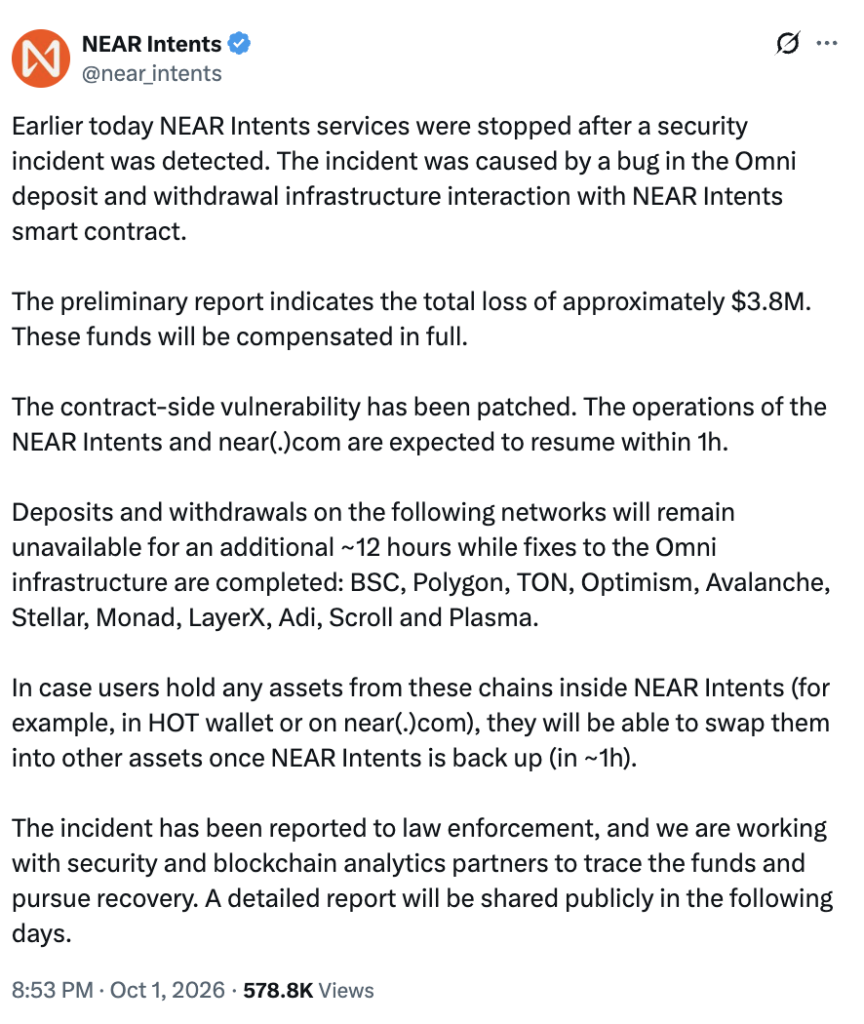
NEAR co-founder Illia Polosukhin said the impact was mainly limited to USDT on BNB Chain. He added that the NEAR mainnet, the NEAR token, and other applications were not directly affected.
About 3.865 million USDT was drained in five transfers
Blockchain analytics firm Bitquery said the attacker withdrew about 3.865 million USDT in five transactions from a BNB Chain vault address used by NEAR Intents between the evening of Sept. 30 and Oct. 1. The process lasted about six hours.
The funds were later swapped into BNB and split across dozens of fresh addresses. As of the afternoon of Oct. 1, Bitquery said it had traced about 99% of the stolen funds, including:
- about 76% converted into 34.69 BTC and spread across four Bitcoin addresses;
- about $802,000 sent to KuCoin addresses;
- about $90,000 converted into Monero-related assets.
ZachXBT said the funds moved to KuCoin before crossing onto Bitcoin
On-chain investigator ZachXBT said early on that NEAR Intents' BNB Chain hot wallet showed unusual outflows. He said the funds were then sent to KuCoin and later bridged onto Bitcoin.
So far, KuCoin has not publicly confirmed whether any related accounts or funds have been frozen. Foreign media outlets said they had contacted KuCoin but had not received an immediate response.
Team says it knows the attacker and opened a 48-hour repayment window
The case saw a new development on Oct. 2. NEAR Intents general manager Alex Shevchenko said the team had identified the attacker and issued a public message: "We know who you are."
The team also published repayment addresses for BTC, BNB, and Solana, giving the attacker 48 hours to return the funds through a "responsible disclosure" process. It said that window would close after the deadline.
Main services are back, but some cross-chain functions remain limited
NEAR Intents and near.com restored core services after the patch was deployed. During the early stage of the incident, deposits and withdrawals across 11 networks were restricted, including BNB Chain, Polygon, and Optimism. The team had estimated that full restoration would take about 12 more hours.
As of Oct. 2, NEAR Intents had partially resumed services. The team also said it was working with law enforcement agencies and blockchain analytics firms to trace the funds and would release a full incident report later.
The flaw was in the deposit-and-withdrawal layer, not the NEAR mainnet
NEAR Intents is an intent-based trading system built in the NEAR ecosystem. It is designed to let users swap assets across different blockchains. The system uses infrastructure such as Omni Bridge to handle deposits and withdrawals between chains.
According to NEAR's official documentation, Omni Bridge is the main cross-chain settlement bridge for NEAR Intents, supporting asset flows across Bitcoin, Ethereum, Arbitrum, Base, Solana, and TON.
The vulnerability was in the interaction between the Omni deposit-and-withdrawal layer and NEAR Intents smart contracts, not in the NEAR consensus layer or the NEAR mainnet itself.
NEAR fell to around $4.9 after the incident surfaced
Market reaction was immediate. After the incident became public, NEAR fell about 6.7% to 9% in a single day, dropping to around $4.9. According to the latest CoinGecko data cited for Oct. 2, NEAR was trading at about $4.98, with roughly $1.47 billion in 24-hour volume. The token was still up about 12.8% over the past seven days.
Platform volume has passed $30 billion
The timing drew attention because NEAR Intents had announced only about a month and a half earlier that cumulative cross-chain trading volume on the platform had surpassed $25 billion. NEAR Intents Explorer now shows cumulative volume above $30 billion, with daily volume ranging from about $80 million to $160 million.
Bitquery also highlighted an unusual detail: after stealing the funds, the attacker used NEAR Intents itself to swap about $822,000 of the stolen assets across chains. In other words, funds taken from NEAR Intents were later moved out through NEAR Intents.
The article was first published by Blockcast, citing an earlier report from Blockcast's source text that said the piece originally appeared in Blockcast's referenced outlet.