
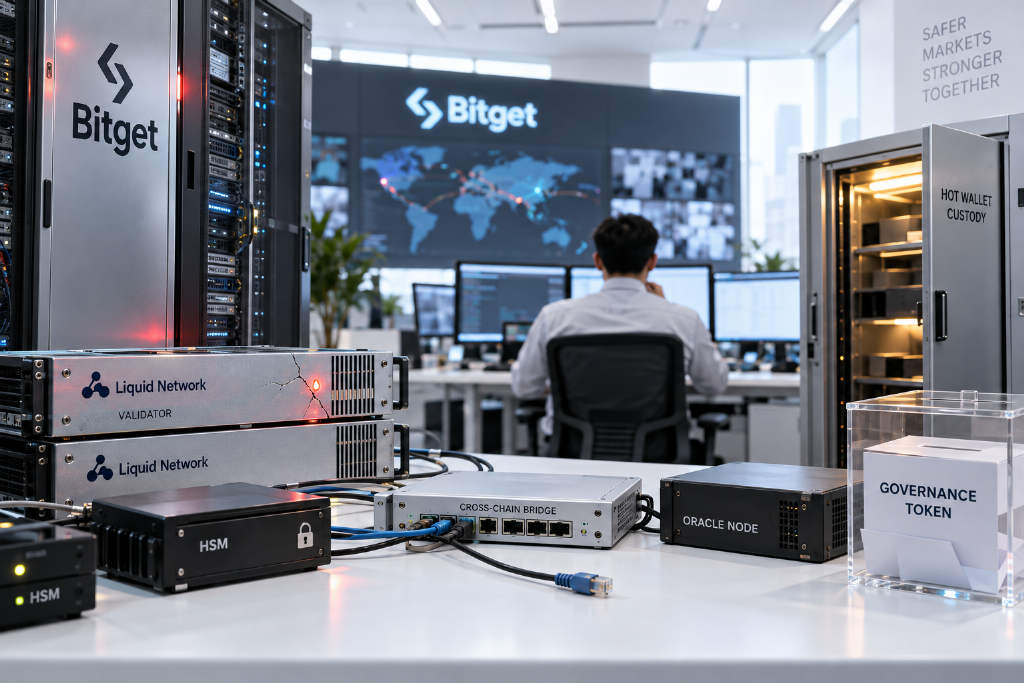
Crypto security incidents caused about $730 million in losses in September 2026, according to a monthly report from ZeroShadow that cited statistics from multiple blockchain security monitoring platforms. The report said the clearest feature of the month was a shift in targeting: exchange backends and core infrastructure became prime attack surfaces.
Two incidents accounted for nearly all of the damage. A backend system manipulation attack involving Bitget hot wallets led to losses of about $387.5 million, while a validation software exploit on Liquid Network caused about $319 million in losses. Combined, the two represented more than 95% of the month’s total, making September the highest-loss month of 2026 so far.
The report added an important distinction. The $730 million figure reflects reported incident scale or fund outflows, not final unrecoverable net losses. In the Liquid Network case, the attacker later returned about 85% of the stolen funds, or roughly $272 million. About $47 million remained unreturned.
Attack patterns moved beyond smart contracts
ZeroShadow said September saw a broad mix of attack methods at the same time: exchange backend manipulation, validator software flaws, governance proposal manipulation, oracle price manipulation, cross-chain bridge balance drains and DEX liquidity pool attacks. The report’s central point was that attackers are moving away from the smart contract layer and toward infrastructure.
Major hacking incidents in September
Bitget hot wallet backend system manipulation
Date: Sept. 25. Reported loss: about $387.5 million.
According to the report, the attacker used a zero-day flaw in a third-party security product to obtain high-privilege internal credentials, forged withdrawal instructions and bypassed risk-control checks. Funds worth about $387.5 million were moved out of Bitget’s hot wallet and warm wallet infrastructure across Ethereum, XRP, BSC, Arbitrum and Avalanche.
Bitget said private keys were not compromised, cold wallets were unaffected and user balances were not impacted. The exchange said the losses were covered by a user protection fund of more than $464 million. It also said affected systems had been isolated, internal credentials had been reset, and multiple security firms were working on the investigation and on-chain tracing.
Liquid Network validation software exploit
Date: Sept. 6. Reported loss: about $319 million.
The attacker exploited a range-proof cache collision flaw in Elements, the validation software used by Liquid Network. The flaw allowed the attacker to mint about 4,000 L-BTC without real asset backing and then redeem real bitcoin through SideSwap’s peg-out mechanism.
The attacker, who described themselves as a white hat, negotiated with Blockstream through on-chain messages. After the flaw was fixed, about 3,400 BTC was returned, equal to roughly 85% of the stolen amount. About 598.5 BTC, or around $47 million, had not been returned.
Neutron governance proposal manipulation
Date: Sept. 22. Reported loss: about $4.4 million.
The report said the attacker spent about 20,199 USDC to buy roughly 31.6 million NTRN, then staked the tokens about 12 minutes before voting closed. A malicious governance proposal passed with about 82% support.
The attacker then gained admin control over 11 contracts, migrated those contracts to malicious code and stole about $4.4 million in assets. Cosmos Hub validators later coordinated a network halt of about 25 hours and moved about 1.23 million ATOM from addresses linked to the attacker as part of asset recovery efforts.
Duelbits hot wallet private key compromise
Date: Sept. 24. Reported loss: about $7 million.
The report said the hot wallet of crypto gambling platform Duelbits was attacked, likely because of a private key leak rather than a smart contract flaw.
The attacker took direct control of the hot wallet and moved about 836 ETH, 1.62 million USDT, 97,000 USDC, 31,500 DAI, 12.4 billion SHIB and 8.1 BTC to a new address. Most of the assets were later swapped into ETH and consolidated into a single address. A Duelbits co-founder confirmed losses of about $7 million, said user funds were safe, and said the platform would remain offline until the investigation was complete and the hot wallet was replenished.
Nostra oracle price manipulation
Date: Sept. 17. Reported loss: about $3.5 million.
The attacker created a fake liquidity pool and paired it with wash trading to push the quoted price of NSTR from about $0.006 to about $49.5, an increase of nearly 8,000x.
Because Nostra’s lending protocol relied on a third-party price source that read the pool’s quote, the attacker used the heavily inflated NSTR as collateral and borrowed about $3.5 million worth of ETH, STRK, USDC, USDT, WBTC and DAI from the Starknet money market. The attacker later bridged about $1.92 million of the stolen assets to Ethereum, including 234.57 ETH and 1.3 million DAI. Nostra suspended lending, withdrawals and liquidations after the incident.
Payy Network cross-chain bridge exploit
Date: Sept. 24. Reported loss: about $1.83 million.
Payy Network’s Ethereum bridge was attacked at 4:21 UTC on Sept. 24, according to the report. The attacker drained the bridge’s full balance, about $1.8 million in USDC, then used privacy protocol Railgun for cover and swapped the USDC into ETH.
Payy Network, described in the report as a rollup project offering on-chain payroll and treasury services, said the lost funds were non-custodial assets deposited by users. It had not disclosed the root cause of the exploit. The project paused all operations after the attack.
Rug pulls and phishing cases
The report listed five representative rug pull or phishing-related incidents.
- On Sept. 16, a victim using an address beginning with 0xe268 lost $565,768 in sUSDat on Ethereum after signing a phishing signature.
- On Sept. 25, a user on Ethereum was hit by an address poisoning attack and lost $67,572 in USDT. The correct address was 0xca16b299700674dda6941baa1bdeeff6d90fd94b, while the mistaken address was 0xca166632d25ea74baa93a5303aa73f61e80fd94b.
- On Sept. 26, a user on XRP Ledger signed a phishing transaction and lost $37,927 in XRP. The victim address was rGtghKcmYY8gdUQwQerY5Ruww2LvdbgWVh.
DYORSWAP fake mainnet phishing case
Date: Sept. 27.
The report said scammers built a fake GIWA mainnet and integrated a false cross-chain RPC into DYORSWAP, tricking users into sending ETH to a fake bridge contract. The total stolen amount was about $2 million. GIWA said its mainnet had not launched, and the DEX project started compensation for affected funds.
Trezor email vendor breach
Date: September.
Trezor’s email service provider, Brevo, was attacked, the report said. After obtaining part of the customer contact database, the attacker sent phishing emails disguised as official security alerts to about 347,000 Trezor users, urging them to download malicious software and enter wallet backup passwords.
The report said the case stood out because the wallet itself was not attacked directly. Instead, the attacker first breached an upstream service provider and then used the exposed user data for targeted phishing.
Robinhood Chain meme coin rug pull series
Time period: July 10 to Sept. 21, disclosed on Sept. 27. Reported losses: at least $18.43 million.
On-chain analysis cited in the report linked the same operating group to at least 53 meme coin issuance projects on one chain. The group allegedly used many related wallets to accumulate more than 70% of token supply early in trading, drew in retail participation through project hype, then sold into that demand. In some projects, internal wallets controlled 82% to 86% of supply.
The investigation said proceeds from one project were used to launch the next, creating a repeated cycle of issuance, concentrated control, attracting buyers, cashing out and issuing again. Total extracted funds were estimated at no less than $18.43 million.
What the report concluded
ZeroShadow said the trend was now clearer: in September 2026, attack targets moved from smart contract vulnerabilities toward lower-level infrastructure. Alongside the Bitget and Liquid Network cases, the report also pointed to a FastSwap liquidity pool flash attack, the 8,000x false quote used in the Nostra oracle manipulation, the drained Payy Network bridge balance and the Duelbits hot wallet key leak as signs of the same shift.
The report argued that attackers are systematically looking for weak points in infrastructure rather than trying to break contract code head-on. In the Bitget case, the attacker obtained internal credentials through a zero-day flaw in a third-party security product, forged withdrawal instructions and bypassed risk controls without touching private keys. In the Liquid Network case, a defect at the validator software layer was enough to put hundreds of millions of dollars at risk.
ZeroShadow’s security team gave three sets of recommendations:
- For individuals: be cautious with crypto links recommended by AI tools, always use official channels, avoid signing transactions with unlimited approvals, and regularly revoke approvals.
- For project teams: raise governance proposal thresholds and add delayed execution, conduct dedicated audits of validator software and cache mechanisms, review data integrity checks in exchange backend authorization systems, and strengthen abnormal trading surveillance in DEX liquidity pools.
- For the industry: build backend security standards for exchanges, improve monitoring of supply-chain risks tied to third-party security products, and keep tracking the evolving tactics of state-level APT groups such as North Korea’s Lazarus Group.