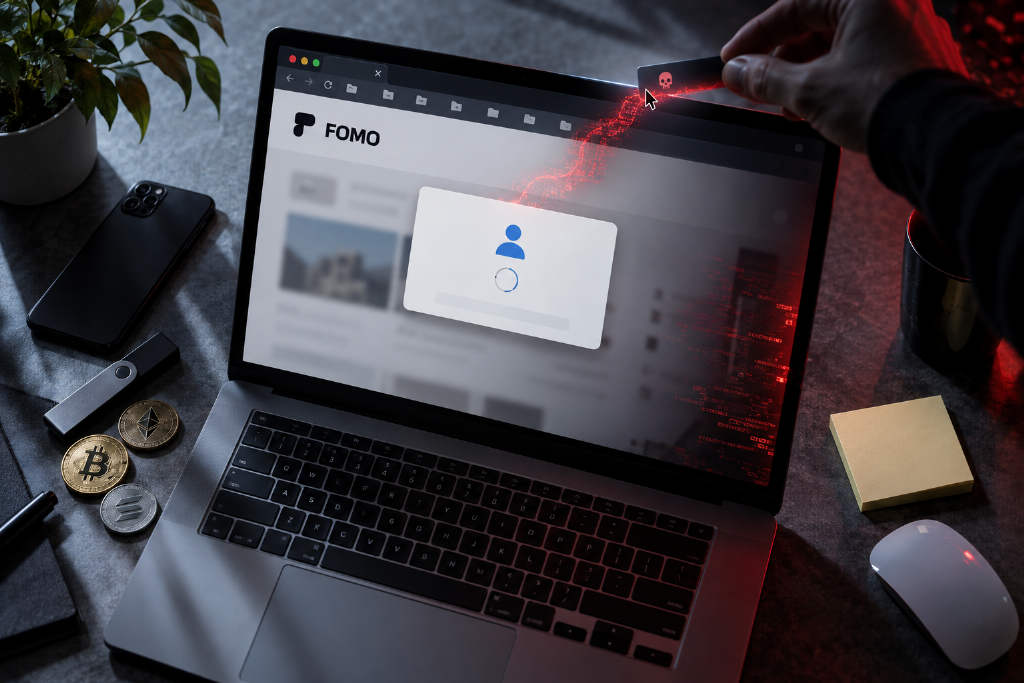
SlowMist researcher Cos warned on Oct. 8 that a bookmark-based phishing attack targeting FOMO’s web interface has begun to appear. According to the alert, the phishing page tricks users into completing a fake human verification step, then asks them to drag malicious JavaScript code into the browser’s bookmarks bar and save it as a bookmark. Once the victim clicks that bookmark two to three times, an attacker can hijack a previously logged-in FOMO account and immediately steal the crypto assets held in it. The warning focuses on a client-side attack flow that abuses browser bookmarks rather than a normal wallet signature prompt, making it a notable security risk for users accessing FOMO through the web.
BlockBeats reported on Oct. 8 that SlowMist researcher Cos has detected bookmark-based phishing attacks targeting FOMO’s web interface.
In this scam, a phishing page prompts users to complete a fake human verification process and drag malicious JavaScript code into the browser’s bookmarks bar, where it is saved as a bookmark.
After the user clicks that bookmark two or three times, a previously logged-in FOMO account can be hijacked by the attacker, and the crypto assets in the account can be stolen immediately.
This article was originally published by Bit.Fan. For more cryptocurrency news and market insights, visit www.bit.fan. Disclaimer:
The market information, project data, and third-party content displayed on this platform are for industry information sharing only and do not constitute any form of investment advice or return commitment.
Cryptocurrency trading carries high risks. Users should fully assess their risk tolerance and make independent decisions. All profits, losses, and legal responsibilities are borne by the users themselves.