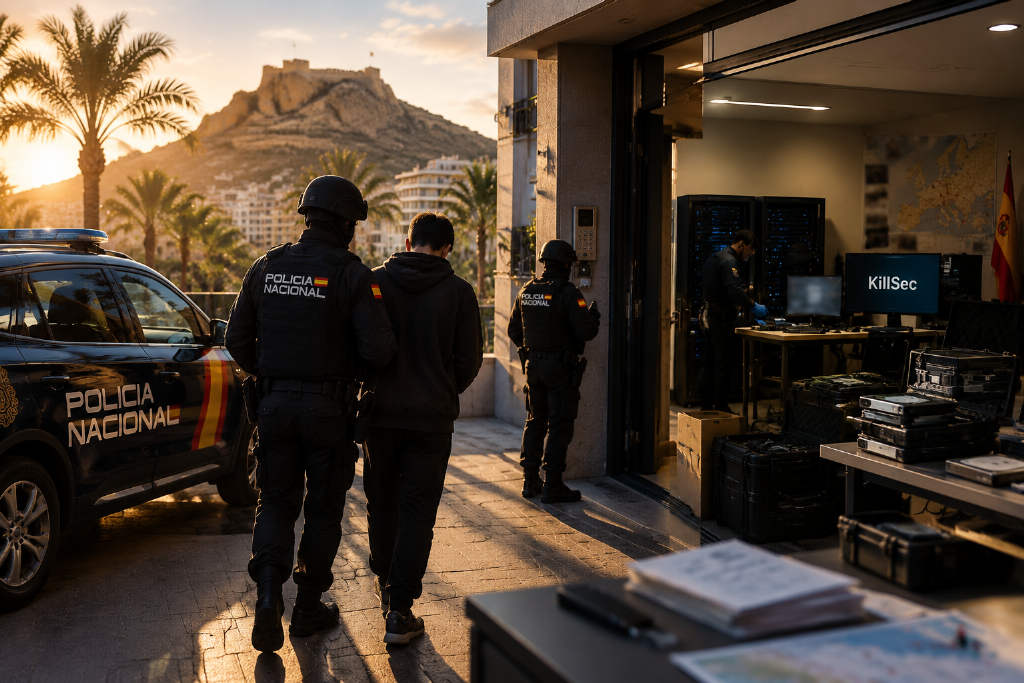
Spanish police arrested a 16-year-old Romanian national in Alicante on suspicion that he served as an administrator and key operator of the KillSec ransomware group, according to an Odaily report citing Decrypt. Europol said law enforcement agencies have taken control of the group’s servers and leak site and secured at least 110 TB of stolen data. The coordinated operation included searches at eight properties across Spain, Greece, Romania, and the United Kingdom. Investigators are reviewing about 1,000 suspected attacks worldwide, with roughly 500 already confirmed as successful. Authorities also arrested two other suspects in their 20s in the UK and Romania. In a separate case tied to the investigation, a Dutch man living in the UK was charged and arrested in Puerto Rico and is awaiting extradition. KillSec has reportedly been active since around 2024, demanding ransom payments in cryptocurrency and using double-extortion tactics by threatening to publish stolen data. Europol’s European Cybercrime Centre provided cryptocurrency tracing and digital forensics support.
Spanish police have arrested a 16-year-old Romanian national in Alicante on suspicion that he was an administrator and a main operator of the KillSec ransomware group.
Europol said law enforcement agencies have taken control of the group’s servers and its leak site, while securing at least 110 TB of stolen data.
The operation included searches at eight properties in Spain, Greece, Romania, and the United Kingdom. Investigators are examining about 1,000 suspected attacks worldwide, and around 500 of those cases have already been confirmed as successful.
Authorities also arrested two other suspects in their 20s, one in the UK and one in Romania. A Dutch man living in the UK was charged and arrested in Puerto Rico and is now awaiting extradition.
KillSec has reportedly been active since around 2024. The group is known for demanding ransom in cryptocurrency and using double-extortion tactics through encrypted servers and threats to publish stolen data. Investigators are tracing the group’s proceeds, including cryptocurrency. Europol’s European Cybercrime Centre provided cryptocurrency tracing and digital forensics support in the case.
This article was originally published by Bit.Fan. For more cryptocurrency news and market insights, visit www.bit.fan. Disclaimer:
The market information, project data, and third-party content displayed on this platform are for industry information sharing only and do not constitute any form of investment advice or return commitment.
Cryptocurrency trading carries high risks. Users should fully assess their risk tolerance and make independent decisions. All profits, losses, and legal responsibilities are borne by the users themselves.