YAM Finance2026-09-02 05:48:03YAM Finance hit by governance takeover attempt targeting Timelock controlYAM Finance is facing a governance takeover attempt, according to monitoring by Defimon. The attacker self-delegated about 504,000 YAM, equal to roughly 3.3% of total supply and slightly above the required proposal threshold, then submitted proposal No. 45 to YamGovernorAlpha. The proposal contains no description and only calls the YAM Timelock contract’s setPendingAdmin function, assigning the role to the attacker’s address. If the proposal passes and is executed, the attacker would become pendingAdmin and could later call acceptAdmin to take full control of the Timelock. That would give the attacker administrative control over all YAM protocol contracts and the DAO treasury. Defimon Alerts said the amount at risk is about $337,000. Because the YAM protocol is currently dormant, YAM holders were urged to vote against the proposal before block height 25897343, which was estimated to be about 34 hours away.830
wallet securi2026-09-01 02:55:47Two Wallets Lose ~$187K Over Unrevoked 2024 Token ApprovalsTwo crypto wallets lost roughly $187,000 after leaving token approvals from 2024 in place, according to Odaily Planet Daily. The first loss involved SYN worth $124,000: the approval was signed in February 2024, the funds arrived on August 30, and they were moved out about 25 hours later. The second involved 62,489 USDC: the approval was signed in July 2024, the funds arrived on August 27, and they were transferred away roughly four days later. Additional details, including the wallets involved, were not disclosed.890
Scam Sniffer2026-09-01 02:53:47Scam Sniffer says two wallets lost about $187,000 after old approvals were left activeScam Sniffer said on Sept. 1 that two wallets lost a combined roughly $187,000 because token approvals signed in 2024 had not been revoked. One case involved SYN worth about $124,000. The approval was signed in February 2024, the funds arrived on Aug. 30, and the tokens were moved about 25 hours later. The other case involved 62,489 USDC. That approval was signed in July 2024, the funds arrived on Aug. 27, and they were moved about four days later. The alert points to the risk of leaving old token allowances in place after assets reach a wallet.890
Injective2026-09-01 00:54:00Injective reportedly halted for about four hours after binary options flaw, with roughly $4.9 million drainedInjective was reportedly paused for about four hours on Sept. 1 after a binary options exploit led to the loss of about $4.9 million, according to PANews, citing X user Paddy-earthling. The account said the attacker abused Frontrunner, a deprecated oracle that remained registered even though its data source had long been cleared. By creating 299 markets tied to that oracle, the attacker allegedly forced a "no price refund" condition and then exploited that refund logic to receive roughly 2x payouts. The stolen USDC was then swapped into about 1,980 ETH, valued at around $4.9 million in the report, and the funds are now sitting in an Ethereum wallet that has never sent any transaction. Paddy-earthling also said Injective’s official X account continued posting marketing content after the incident without mentioning the chain halt. The post added that Injective made its core chain code private, while the attacker was still able to identify the issue through the public SDK. According to the same disclosure, the protocol-level shortfall has already been covered, but the remediation process involved no governance vote and no public explanation, leaving the fix unverifiable from the outside. The author also disclosed holding a long INJ position.850
Fogo2026-08-31 15:20:58Fogo mainnet halts for about 46 hours after foundation attack sends 4 million FOGO to attacker addressFogo’s mainnet has stopped producing blocks for about 46 hours since Saturday afternoon after the Fogo Foundation was attacked and 4 million FOGO tokens were transferred to an attacker-controlled address, according to ChainCatcher. The amount accounts for about 10.3% of the token’s circulating supply. The foundation initially said the chain itself was unaffected, but the network was later paused 15 hours afterward, with the team planning an upgrade to restrict the related addresses. Fogo’s official explorer shows block 718,525,971 as the last block, its RPC endpoint is returning a 502 error, and DefiLlama data shows the chain’s TVL frozen at $987,000 for three straight days. KuCoin and Gate have disabled FOGO deposits and withdrawals while keeping trading open. Fogo also warned users about a fake compensation voting link posted by an impersonation account, @FcgoFNDN. The foundation has not yet released attack details, a compensation plan, or a restart timetable.910
SlowMist2026-08-31 13:24:49SlowMist’s Cos Says Private Key Leak Tied to Group Theft, Hacker Made About $200,000According to ChainCatcher, SlowMist’s Cos has flagged a hacker address linked to a group theft incident that affected more than 100 addresses and dozens of real users. The reported cause was a private key leak, and the hacker is estimated to have made about $200,000 from the attack. Cos also said the actors involved were not new, describing them as an old group. Affected users may try to identify common factors across the compromised wallets and accounts. No additional details on the attacker’s identity, the exact theft method beyond the private key leak, or the timeline of the incident were disclosed in the brief. The update was published as a 7x24 flash report by ChainCatcher.780
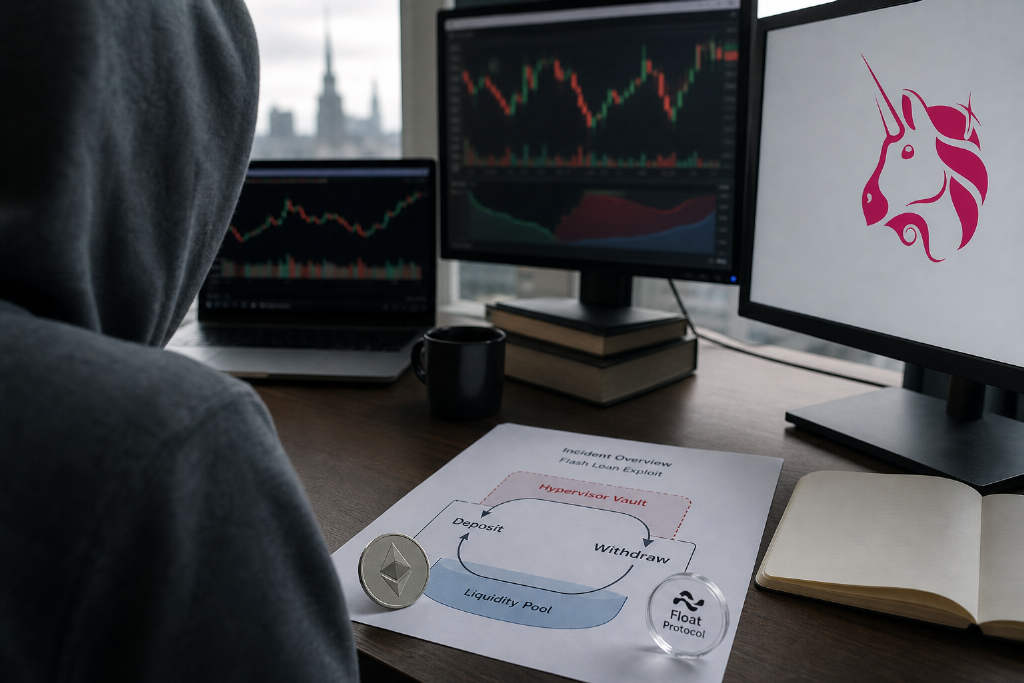
Float Protoco2026-08-31 10:42:06Float Protocol hit by flash loan attack, losing about $28,000, SlowMist saysFloat Protocol suffered a flash loan attack that caused losses of about $28,000, or 10.71 ETH, according to monitoring data cited by ChainCatcher from blockchain security firm SlowMist. The attacker manipulated the Uniswap V3 spot price, specifically slot0, which led to incorrect LP share pricing in the protocol’s Hypervisor contract. SlowMist said the issue was tied to key functions that lacked TWAP or oracle validation as well as slippage protection. The attacker then carried out large trades in a V3 pool to distort the values returned by currentTick() and getTotalAmounts(). After pushing share valuations higher, the attacker repeatedly deposited and withdrew to extract profit. The report focuses on the attack path and the pricing weakness involved in the exploit.850
GoPlus Securi2026-08-29 12:17:03GoPlus: GOLD Token Developer Funds Traced to KuCoin, PLATINUM Contract Can Drain WalletsGoPlus Security has issued an alert about a token operation traced back to major exchanges. The developer behind the GOLD token received initial funds that can be traced to KuCoin, while 15 wallets linked to market manipulation trace back to Binance. The same group also deployed Trump Digital Platinum (PLATINUM). The token contract can arbitrarily transfer a holder's entire balance, GoPlus said, urging users not to buy it.780