security brea2026-09-05 21:43:40XRPH Wallet Hit by Security Breach, Loss Amount UnknownXRPH Wallet has experienced a security vulnerability that led to unauthorized transactions. Multiple users reported compromised accounts, resulting in losses of XRPH and XRPHAI tokens. The exact financial impact has not been determined. The development team is investigating the root cause and tracking stolen funds. XRP Healthcare has urged users to stop using the wallet immediately and is collaborating with partners to freeze and recover affected assets. The team promised to release detailed information after confirmation. The cause and scope are still under investigation. The news was reported by U.Today and Techub News.850
SlowMist2026-09-04 12:10:49SlowMist flags iPhone Safari attack chain using six patched DarkSword flawsSlowMist said it has identified an attack campaign disguised as a free VPS service that targets iPhone Safari on devices running iOS 18.4 through 18.6.2. According to the security team, the attackers chained six vulnerabilities under the codename DarkSword to build a full intrusion path, covering WebKit remote code execution, sandbox escape, and kernel read-write access. The campaign could extract app container files and keychain data without the user noticing, and log keyboard input when wallets such as imToken, TokenPocket, or TronLink were open in the foreground. SlowMist said all six vulnerabilities have already been fixed by Apple and described the activity as reuse of an n-day exploit chain. The team also said that simply visiting a malicious page does not by itself prove that a mnemonic phrase or private key was stolen, and that device forensics would still be required to confirm any compromise. Users on iOS and iPadOS were advised to upgrade to version 18.7.3 or 26.3 and later.920
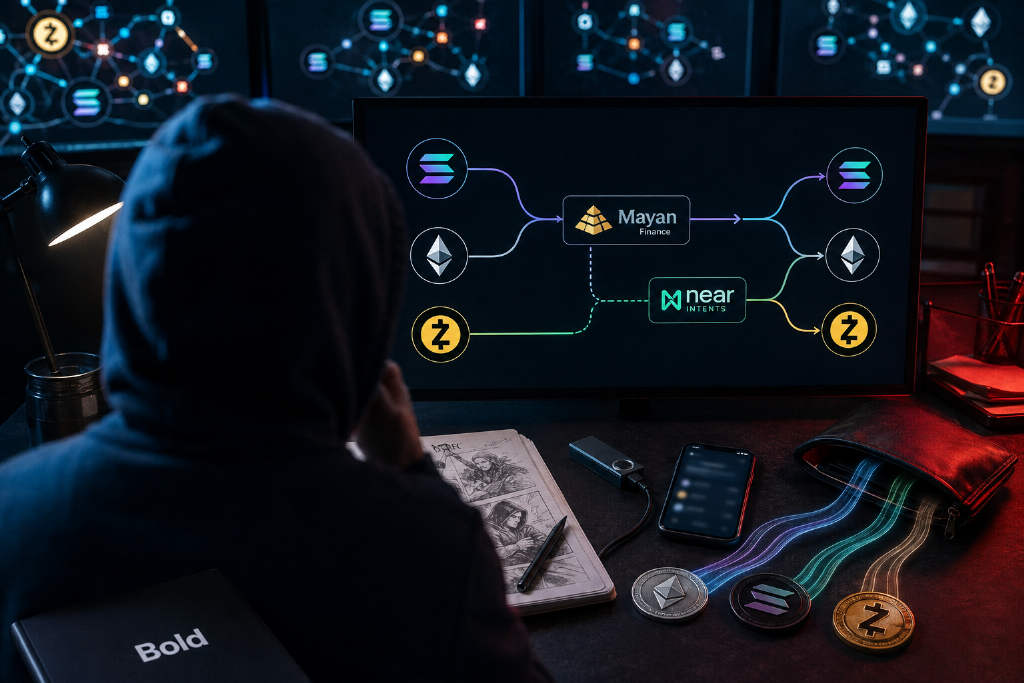
wallet securi2026-09-04 10:44:46Crypto Comic Creator Bold's Wallet Hacked, ZachXBT Tracks Stolen FundsCrypto comic creator Bold reported a wallet hack with all funds stolen. On-chain detective ZachXBT tracked some of the stolen assets, including $51,000 swapped to ZEC, $43,000 to ETH, and $43,000 bridged from Solana to Ethereum via Mayan Finance. Additionally, 480 SOL were transferred via Near Intents, and 51 ZEC were moved to a shielded address via Near Intents. The incident highlights the ongoing security challenges in the crypto ecosystem.870
USDC2026-09-04 04:14:18USDC’s quantum migration problem spans 37 blockchains, and Circle cannot solve it aloneCircle has warned that the quantum resources needed to break mainstream blockchain signature schemes are falling, citing a low-resource record of 813 logical qubits. But the core issue for USDC is not Circle’s own systems alone. According to the company’s current contract documentation, USDC is deployed across 37 mainnets, which means any credible post-quantum migration would also depend on host chains, wallets, custodians, bridges, and end users adopting safer authorization methods. The report argues that the 813-qubit figure is a reference point, not a countdown clock. It reflects improving circuit efficiency, yet does not by itself describe attack depth, error-correction costs, runtime on physical hardware, or when such hardware might exist. It also challenges Circle’s comparison between attack-oriented logical qubits and Google’s Willow, which was described by Google as a 105-qubit processor rather than 105 logical qubits usable for cryptographic attacks. Circle’s Arc stack may help test post-quantum verification, including an SLH-DSA-SHA2-128s precompile, but it does not automatically replace transaction signing across public networks. The article’s conclusion is that USDC’s quantum security will require coordinated changes across 37 independent network paths, not a unilateral switch by the issuer.890
Coldcard2026-09-03 09:31:07Coldcard exploiter moves stolen BTC through THORChain and swaps part into ETHA hacker tied to the third wave of Coldcard wallet thefts has begun moving stolen Bitcoin onchain, swapping part of the haul for Ether through THORChain. Galaxy Research head of research Alex Thorn said the exploiter moved roughly 10% of the stolen funds, while about 90% remains untouched. Thorn described the transfers as the first onchain movement from the original hacker addresses across all three waves of the Coldcard thefts. According to Thorn, the attacker appears to be struggling to swap the full amount through THORChain, with transactions being refunded and retried. Onchain analysts traced the funds to a new Ethereum address, which Thorn said he shared with relevant authorities and crypto companies. He added that it is still unclear whether the attacker will try to further obscure the trail or move the assets through an exchange. Galaxy Research previously linked the Coldcard exploit to the theft of at least 1,789 BTC from 8,865 addresses, worth about $114.7 million at the time of the theft. CertiK said in August that hackers connected to the exploit had also sent 64 BTC and 200 ETH to mixers including Tornado Cash.950
wallet securi2026-09-01 02:55:47Two Wallets Lose ~$187K Over Unrevoked 2024 Token ApprovalsTwo crypto wallets lost roughly $187,000 after leaving token approvals from 2024 in place, according to Odaily Planet Daily. The first loss involved SYN worth $124,000: the approval was signed in February 2024, the funds arrived on August 30, and they were moved out about 25 hours later. The second involved 62,489 USDC: the approval was signed in July 2024, the funds arrived on August 27, and they were transferred away roughly four days later. Additional details, including the wallets involved, were not disclosed.870
Scam Sniffer2026-09-01 02:53:47Scam Sniffer says two wallets lost about $187,000 after old approvals were left activeScam Sniffer said on Sept. 1 that two wallets lost a combined roughly $187,000 because token approvals signed in 2024 had not been revoked. One case involved SYN worth about $124,000. The approval was signed in February 2024, the funds arrived on Aug. 30, and the tokens were moved about 25 hours later. The other case involved 62,489 USDC. That approval was signed in July 2024, the funds arrived on Aug. 27, and they were moved about four days later. The alert points to the risk of leaving old token allowances in place after assets reach a wallet.870
Ethereum2026-08-31 14:15:15ChainFeeds PRO Reviews ePBS, Verifiable UTXO Discovery, and the Limits of RISC-V Instruction MeteringChainFeeds Research’s latest PRO issue brings together a wide set of protocol and research updates across Ethereum and Bitcoin. The edition highlights Ethereum’s planned introduction of enshrined proposer-builder separation, or ePBS, through EIP-7732 in the Glamsterdam upgrade, arguing that the change could reduce protocol reliance on relays while leaving core MEV market concentration issues unresolved. It also examines two wallet entropy-generation methods designed to reduce dependence on opaque software random number generators, alongside a Bitcoin Optech roundup covering a Core Lightning security release, an opt-in replay protection proposal for potential Bitcoin forks, and the gradual wind-down of Hardware Wallet Interface. On the Ethereum research side, the issue reviews a proposal that combines EIP-8304 with UTXO Proof Tables to let wallets verify UTXO discovery without fully trusting RPC providers, and a RISC-V execution study showing that identical instruction counts can still produce large timing differences across workloads and hardware. The report also notes a post-quantum migration idea for ecrecover, a set of MEV research summaries from Flashbots, and a paper on migration paths to post-quantum cryptography for Bitcoin, Ethereum, and Solana.1110