
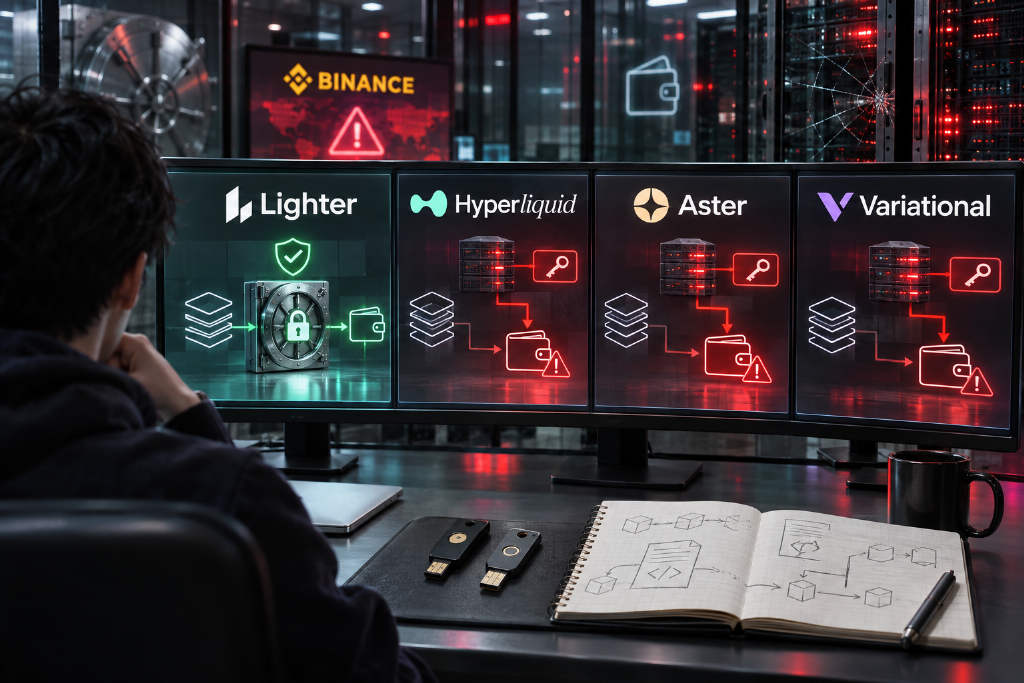
After the Binance hot wallet theft, researcher jaehaerys posted a breakdown on X of the contract structures behind four perpetual DEXs: Lighter, Hyperliquid, Aster, and Variational. The question he focused on was simple: if a protocol’s internal systems were compromised in the same way, could users still get out safely, or could an attacker drain balances anyway.
His conclusion was blunt. Of the four, only one protocol could prevent an attacker from directly withdrawing user funds.
Four perpetual DEX designs under review
In the X thread, jaehaerys listed the rough scale of funds involved: about $1 billion for Lighter, about $6.5 billion for Hyperliquid, about $500 million for Aster, and about $290 million for Variational. His review did not center on whether the front end looked decentralized or whether trades were recorded on-chain. He looked at whether users could still protect their assets if the team’s systems were breached.
Lighter: tighter withdrawal controls and a forced exit path
Jaehaerys described Lighter as the design that comes closest to decentralization among the four. Withdrawals require ZK proof verification, and standard withdrawals can only be sent to the wallet address bound to the user’s first deposit. Under that setup, he said, a server compromise alone would not let an attacker move user balances out.
The protocol also includes a forced withdrawal mechanism. If a withdrawal is not processed within 14 days, anyone can trigger what he called “desert mode,” allowing all users to exit.
He did not present Lighter as fully trustless. Prices are still supplied by the operator, and a 3/5 multisig together with a 4/7 security council can change the code without notice.
Hyperliquid: 86% of USDC sits in a Coinbase single-key wallet
His critique of Hyperliquid focused on custody. According to jaehaerys, 86% of the roughly $6.5 billion in USDC is held in a single-key wallet under Coinbase. That means fund safety depends on Coinbase’s custody practices, and that part cannot be verified on-chain.
He also wrote that the Hyperliquid chain can execute system transactions without going through the Coinbase private key. On the validator side, five validators run by the Hyper Foundation account for 47% of staked assets, and the node software is closed source.
Aster and Variational: still custodial at the core
For Aster, he said each withdrawal must be initiated by an operator address and approved by two keys. In that structure, a user signature only proves that a withdrawal was requested; it does not protect the pool itself.
Aster does have an hourly withdrawal cap, but the same 4/7 multisig can immediately change roles and adjust the cap.
Variational, in his description, is even more permissive. Any one of 17 operational keys can move USDC from any pool, there is no amount limit in the contract, and users have no forced exit mechanism.
A DEX label is not a safety guarantee
Jaehaerys ended the thread with a broader warning. A perpetual DEX may have a decentralized front end and on-chain trading, but user funds can still remain under the control of team keys or operator addresses.
Before sizing up positions, he said users should verify two things: where the funds are actually held, and whether they can exit on their own if the team is unavailable. In his framing, contract permissions and exit routes matter more than the DEX label itself.



