
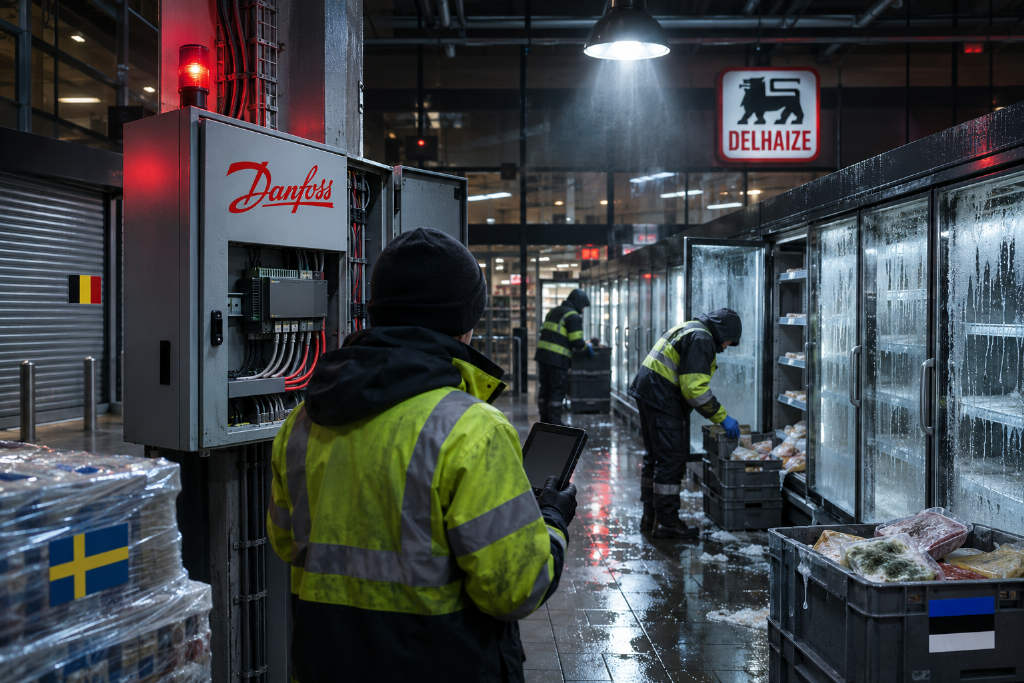
Hackers remotely altered refrigeration control settings at supermarkets across several European countries in the early hours of Nov. 2, causing refrigerator and freezer temperatures to rise, according to The Hacker News. Stores in Belgium, Sweden and Estonia were affected, and some locations were forced to discard food or remove products from sale. As of Monday evening, no group had claimed responsibility.
Remote changes pushed equipment into unsafe temperature ranges
Danfoss, the Danish manufacturer of refrigeration control systems, said the attack matched the pattern seen three weeks earlier when hundreds of supermarkets in France were hit.
Stephan Moelans, chief executive of Belgian refrigeration contractor Sabcobel, said the attackers switched refrigeration equipment at Delhaize supermarkets into defrost mode, which caused temperatures to climb. At an ICA supermarket in Sjöbo, Sweden, refrigeration equipment was reportedly set to 50 degrees Celsius, leaving staff with no option but to throw away affected goods.
Luc De Laet, who owns a butcher shop in Hove south of Antwerp, said the temperature in his cold storage was raised to 18 degrees Celsius. He estimated losses at about 15,000 euros worth of meat. Musgrave took products off shelves as a precaution.
Default passwords and outdated software cited as key weaknesses
A Danfoss spokesperson said the compromised systems were still using default passwords and had not been deployed on secure networks, describing those issues as the main reasons the devices were breached. The company also said customers that had not updated passwords and software were affected because the software versions were outdated.
Jann Mutso, chief executive of Kitman Coldtech, confirmed that the systems hit in Estonia were older Danfoss installations.
CERT-FR says the campaign may still be active
France's cyber agency CERT-FR issued an alert saying attacks targeting Danfoss AK-SM and AK-SC series systems, along with Copeland xweb and Dixell xweb controllers, may still be ongoing. When The Hacker News checked the alert on Nov. 3, it found the record had last been updated on Oct. 16.
For devices that have not yet been compromised, the guidance is to disconnect them from the internet as a priority and remove all public IP access. Before cutting data transmission, operators are advised to review insurance contract terms. They should also inspect all configurations, including defrost schedules, and move connections to a secure VPN channel.
Operators were also told to update firmware regularly. For Danfoss equipment, that includes setting the security level to "strict" and changing default passwords. IP filtering at the firewall level was described only as an emergency fallback. If a device has already been compromised, operators must reboot Danfoss equipment or restore factory settings, then reconfigure security parameters before reconnecting it.
French, Belgian and Swedish authorities are responding
CERT-FR had already issued an alert in October, saying attacks against Danfoss AK-SM and AK-SC series systems, as well as Copeland xweb and Dixell xweb controllers, could still be in progress. Danfoss said at the time that most of the affected devices in France were older models that no longer received updates, including the AK-SM 800 and AK-SC 355.
Sweden's National Cyber Security Centre has advised companies to inventory internet-connected devices and make sure those systems are updated and protected by multiple layers of security. The Belgian Federal Prosecutor's Office has opened a criminal investigation, and Sweden's National Cyber Security Centre is sharing information with agencies across the Nordic region and Europe. As of publication, the identity of the attackers remained unknown.



