Kelp2026-09-15 06:11:44Kelp Freezes rsETH Transfers for One Address for 24 Hours, Says Token Remains Fully BackedEthereum restaking protocol Kelp said on Sept. 15 that it detected suspicious activity involving an address that received rsETH several hours earlier and has placed a temporary 24-hour pause on that address. During the restriction window, rsETH cannot be transferred into or out of the address. Kelp said its contracts remain secure and that rsETH is still fully collateralized. The protocol added that minting, withdrawals, and integrations are operating normally, and users do not need to take any action. The update followed an earlier alert from Blockaid, which said an unidentified user’s Safe wallet on Ethereum had been compromised. Confirmed losses currently stand at about $7.73 million in rsETH. The statement limits the action to a specific address rather than describing a protocol-wide shutdown.700
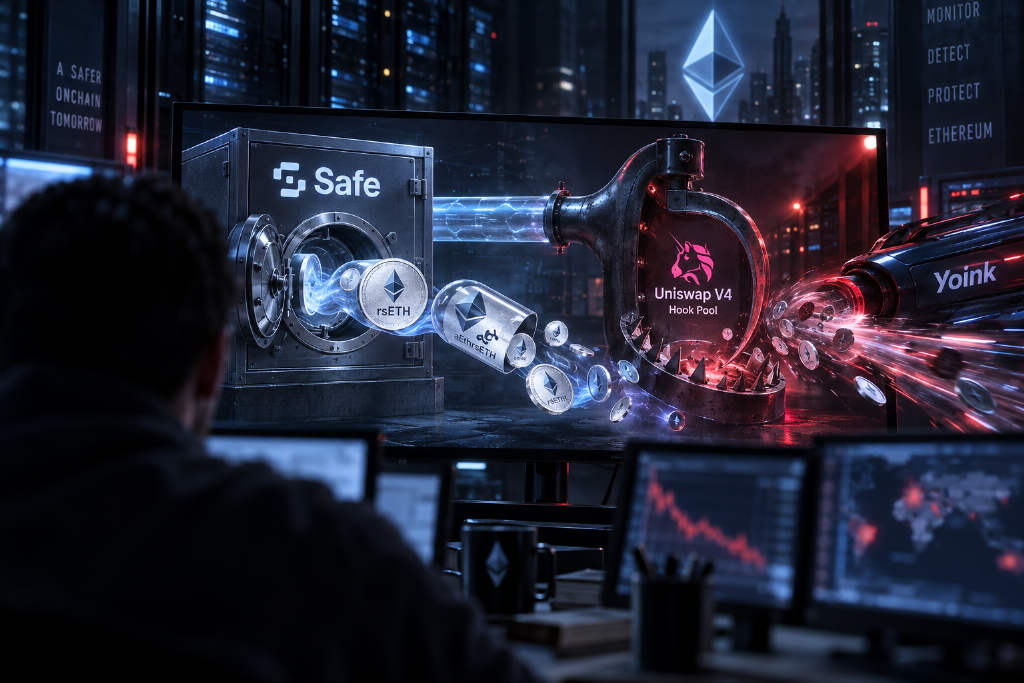
Uniswap V42026-09-15 05:46:31Uniswap V4 Hook exploit drains about $7.73 million from a Safe walletA Safe wallet on Ethereum belonging to an unidentified user was exploited, with confirmed losses of about $7.73 million in rsETH, according to monitoring cited by BlockBeats from Blockaid. The attacker reportedly used a public Keeper Multicall to redirect a custom Uniswap V4 LP module in the Safe to a Hook Pool created by the attacker. From there, a malicious Hook was used to unwrap aEthrsETH into rsETH. The assets were then extracted by Yoink MEV within the same block. The report did not identify the wallet owner and only described the loss as currently confirmed at around $7.73 million in rsETH.800
Blockaid2026-09-15 05:36:57Blockaid spots Ethereum attack on Safe multisig wallet with about $7.73 million in rsETH lossesBlockaid said it detected an attack on Ethereum targeting a Safe multisig wallet belonging to an unidentified user. According to the monitoring firm, the attacker used a public keeper multicall to introduce a custom Uni V4 LP Safe module into a hook-enabled liquidity pool that the attacker had created. The hook then unpacked aEthrsETH into rsETH, after which Yoink MEV extracted the funds within the same block. Blockaid said two transactions have so far been confirmed in connection with the incident. The confirmed loss stands at about $7.73 million in rsETH. No further details about the wallet owner were disclosed in the source material. The report identifies the sequence of contracts and on-chain actions involved in the exploit, including the use of the public keeper multicall, the custom Safe module, the hook-enabled pool, the conversion from aEthrsETH to rsETH, and the block-level extraction by Yoink MEV.670
MetaMask2026-09-14 14:03:11MetaMask Rolls Out New Scam Defenses Across Mobile App and Browser ExtensionMetaMask has introduced a new set of wallet security features aimed at reducing crypto scam losses across its mobile app and browser extension. Announced Monday, the update adds alerts for lookalike wallet addresses, investment and romance scams, and transfers to first-time recipients, while also making transaction review screens clearer. A separate feature called Added Protection will automatically revert transactions if the final transaction does not match what the preview showed; it will launch on the browser extension first, with mobile support coming later. Martin Peko, Staff Product Manager at MetaMask, told Decrypt the company found that many users were bypassing scam warnings because they either strongly trusted the recipient or were being coached through the process. MetaMask is also adding a route to priority support from that warning flow so uncertain users can reach a person. Peko said the wallet is working with security partner Blockaid, which uses large language models, classification models, and analysis of websites, social feeds, onchain bytecode, and transaction flows to identify phishing, scam, and malicious activity in real time. The rollout comes as U.S. authorities continue targeting services tied to investment and romance fraud, and as MetaMask prepares for Consensys’ planned split of its consumer and institutional businesses by the end of 2026.440
Symbiosis2026-09-13 16:12:17Symbiosis Bitcoin bridge flaw let attacker mint syBTC worth a notional $46.1 billion, cash out about $336,000Blockaid said a flaw in the Bitcoin bridge used by cross-chain protocol Symbiosis allowed an attacker to mint roughly 2^62 syBTC to a newly created externally owned account. Using an 8-decimal calculation, the notional face value of the minted amount was about $46.1 billion. The attacker then sold about 4.39 WBTC on Uniswap V4 on Ethereum, realizing about $336,000. Symbiosis said the attack took place at around 04:28 on Sept. 11. The team has paused BTC routing, while other routes remain operational and were not affected. It also said it recovered about 15 BTC and moved the funds into a team-controlled multisig wallet. At the same time, the protocol offered the attacker a white-hat bounty equal to 20% of the funds involved, with a deadline of Sept. 13. The report added that Liquid Network, Nomic and Symbiosis have all seen recent security incidents involving the minting of tokens without real asset backing to expand supply. As of Sept. 13, Symbiosis had not published a technical postmortem for BridgeV2, the final loss amount, or confirmation on whether the attacker accepted the bounty.1010
Symbiosis2026-09-13 16:12:51Symbiosis halts BTC route after Blockaid flags bitcoin bridge minting flawBlockaid said it found a vulnerability in the bitcoin bridge of cross-chain protocol Symbiosis, where an attacker minted about 2^62 syBTC to a newly created externally owned account. Using an 8-decimal calculation, the face value was roughly $46.1 billion. The attacker then sold about 4.39 WBTC on Uniswap V4 on Ethereum, cashing out around $336,000. Symbiosis said the attack took place at about 4:28 on Sept. 11. The team has suspended the BTC route, while other routes remain operational and were not affected. It also said it recovered about 15 BTC and moved the funds into a team-controlled multisig wallet. The protocol is offering the attacker a white-hat bounty equal to 20% of the funds, with a deadline of Sept. 13. As of Sept. 13, Symbiosis had not published a BridgeV2 technical post-mortem, the final loss amount, or confirmation on whether the attacker accepted the bounty. The incident came during a period in which Liquid Network, Nomic and Symbiosis each saw security events involving supply expansion through minting tokens without real asset backing.1240
Blockaid2026-09-11 05:18:02Blockaid says Symbiosis was attacked on BSC, with about $336,000 in WBTC already cashed outBlockaid said it detected an attack involving cross-chain protocol Symbiosis on BNB Smart Chain, or BSC. According to the security firm, a transaction signed by BridgeV2 moved about 2^62 raw syBTC into a newly created externally owned account, or EOA. Blockaid said the token used 8 decimals and carried a face value of about 46.1 billion. The same beneficiary then sold roughly 4.39 WBTC on Ethereum’s Uni V4, the firm said. As of the latest update cited in the post, the attacker had already converted about $336,000 worth of WBTC into cash. The information was attributed to Blockaid’s on-chain monitoring and was published through its X account. No additional details on the exploit method or wider impact were provided in the source material.1100
Optimism2026-09-07 06:11:04Blockaid Detects Attack on Cozy Protocol on Optimism, Losses ~$170KBlockaid has detected an attack on the DeFi risk management protocol Cozy on Optimism, with losses of approximately $170,000 so far.1080